0498 70 98 60
Hacked WordPress Repair Las Vegas: Clean the Site, Then Check What Nevada Expects
A hacked site in Las Vegas rarely fails on a quiet Tuesday. It tends to surface when traffic peaks: the week before a convention, a fight weekend, the launch of a new show. Hacked WordPress repair Las Vegas businesses can count on has to do two things at once: get the site clean and selling again, and help you work out whether the incident triggers obligations under Nevada law. Référenceur handles WordPress cleanups remotely from Belgium and Luxembourg. Our team’s native language is French and its daily working language is English, which also means we can check and repair the French pages that Quebec and European visitors see. To get started, report your hacked site and we will review it at no cost.
If you want a first reading right now, the free scanner below checks your WordPress site for common warning signs.
Why WordPress Sites Here Break at the Worst Moment
The numbers explain why a site that looked fine last month can be compromised today. In its State of WordPress Security in 2026 report, Patchstack logged 11,334 newly disclosed flaws across WordPress plugins, themes, and core during 2025, up 42% from 2024. About 91% sat in plugins and 9% in themes, while WordPress core had only six. Worse, 46% had no developer fix available when they were made public, and for the most heavily exploited flaws, the weighted median time to a first attack was five hours.
Las Vegas adds its own pressure, which is why WordPress malware removal in Las Vegas so often happens against the clock. Booking plugins, ticket forms, event calendars, and table-reservation tools are exactly the kind of add-ons that collect data and get exploited. A hack that injects a redirect during convention week costs more than the cleanup: it costs the inquiries you would have received.
The city also knows what a serious breach looks like. In an October 5, 2023, filing with the SEC, MGM Resorts estimated that a cybersecurity issue identified in September would cut Adjusted Property EBITDAR, its main measure of property earnings, at its Las Vegas Strip and regional operations by about $100 million in the third quarter of 2023. That attack had nothing to do with WordPress, but it made data security a local headline, and customers here notice when a site behaves strangely.
The First 48 Hours, Window by Window
Every incident differs, and these windows are typical, not promised. They depend mostly on how quickly we receive hosting access.
| Window | What we do | What we need from you |
|---|---|---|
| First hours | Snapshot of the infected site, all passwords and keys rotated, malicious redirects stopped | Hosting, WordPress admin, and DNS access |
| Day 1 | Entry point traced through logs, injected files and rogue admin users removed | Confirmation of who should have an account |
| Day 2 | Database cleaned, plugins and themes updated or replaced, firewall rules added | Approval to remove plugins you no longer need |
| Following days | Google review requested, search results monitored, written incident summary delivered | A contact person for any legal follow-up |
Restoring an unchecked backup is a common mistake. The attacker’s backdoor is often already in it, and the infection comes back. Even before we log in, our first-hour guide for hacked WordPress sites lists what you can safely do yourself. The step-by-step article on WordPress malware removal shows what the cleanup involves under the hood.
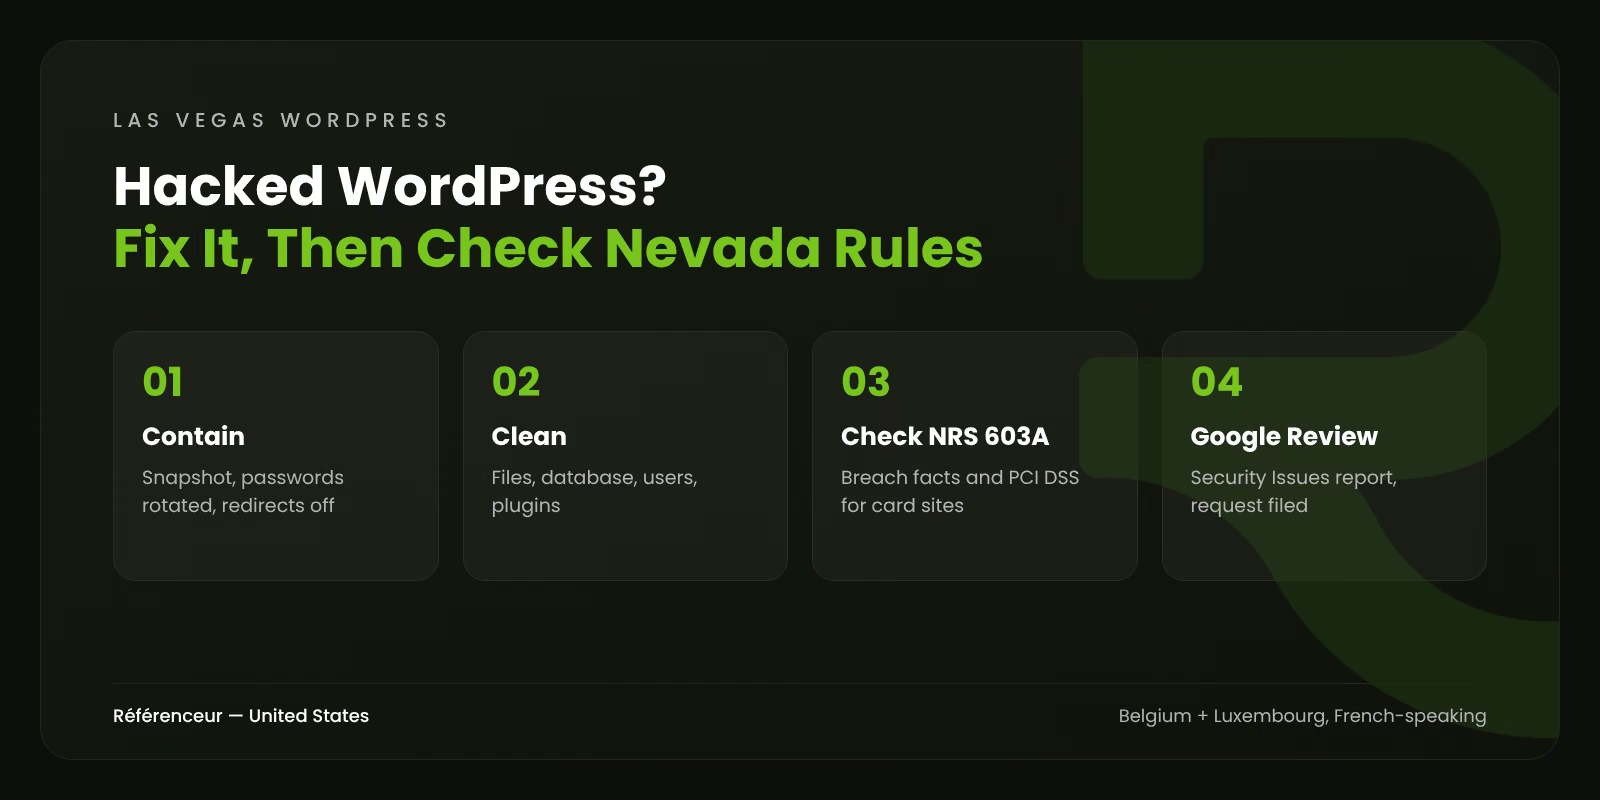
Nevada Law After a Hack: NRS 603A in Plain English
Once the site is clean, the next question is whether personal data was exposed. Nevada’s main rules sit in Chapter 603A of the Nevada Revised Statutes. A short summary of the sections most site owners ask about:
- NRS 603A.210: a business that keeps records containing Nevada residents’ personal information must implement and maintain reasonable security measures to protect them.
- NRS 603A.215: a data collector doing business in Nevada that accepts payment cards must comply with the current Payment Card Industry Data Security Standard (PCI DSS) for those transactions.
- NRS 603A.220: after a breach of personal information, affected Nevada residents must be notified “in the most expedient time possible and without unreasonable delay.” Notice can be delayed if law enforcement says it would impede a criminal investigation, and if more than 1,000 people must be notified at once, nationwide consumer reporting agencies must be told as well.
Whether your incident counts as a breach under these definitions depends on what data the site held and what the attacker reached. Our job is technical: logs, a timeline, and a clear account of what was and wasn’t accessible. Use those facts with your attorney. This page is not legal advice. Our guide on handling a WordPress data breach explains how to document the incident.
Booking Plugins, Card Payments, and Forms: Where We Look First
A Las Vegas site that sells experiences collects more than a brochure site does. We start where the risk is highest:
- WooCommerce checkouts and payment gateways, since a skimming script on the checkout page is among the most damaging infections a store can carry, and NRS 603A.215 makes PCI DSS compliance a legal matter for card-accepting businesses in Nevada.
- Booking and ticketing plugins for shows, tours, and wedding chapels, which store names, dates, phone numbers, and sometimes passport details for international guests.
- Contact and quote forms, including the email settings behind them, so your confirmations don’t land in spam folders and the form can’t be hijacked to send spam.
- Plugins with known flaws or no recent updates. Our list of vulnerable WordPress plugins shows the patterns we watch for.
After the cleanup, run the scan again to confirm the warning signs are gone, or send us the results if anything still looks wrong.
Getting Google’s Warning Removed
If Google flags your site, the details appear in the Security Issues report in Search Console. Google groups problems into three types: hacked content, malware and unwanted software, and social engineering. Once every affected page is fixed, the site owner requests a review from that report, describing the issue, the steps taken, and the result. Google’s help page warns that reviews may need several days and sometimes several weeks, and the requester gets an email when it is received and another when it is complete. Fixing only some pages doesn’t produce a partial return to search results.
We write the review request for you and follow it until Google closes it. For the full sequence, read our article on removing a Google warning from a WordPress site.
When French-Speaking Visitors See the Hack First
Some malware hides from the site owner. It shows spam or redirects only to visitors arriving from search, from a phone, or from certain countries. On a bilingual site, the French pages are sometimes infected while the English ones look normal, or spam pages appear in a language directory no one on your team checks.
That is where our background helps. We read French natively, so we can audit your French pages, translated menus, and language-switching plugin as carefully as your English ones. If guests from Quebec or Europe received spam in your name, we can draft a clear French notice for them, ready for your attorney to review.
If you need to fix a hacked website in Las Vegas because it is down, redirecting, or flagged, act today. You will be working with a team from Belgium and Luxembourg that cleans WordPress sites in English and French and explains every step on a video call, at an hour that suits Pacific Time. Get a Free Assessment. To see our full method, visit our hacked WordPress site repair service, our Las Vegas digital marketing page, or our French market marketing work if your site serves French-speaking customers.
Frequently Asked Questions About Hacked WordPress Repair in Las Vegas
Do We Have to Tell Customers About the Hack Under Nevada Law?
The notice duty in NRS 603A.220 turns on whether personal information, as the statute defines it, was exposed in a breach. Many hacks inject spam or redirects without touching customer data. Others reach order records or form submissions. We establish the technical facts; your attorney decides whether notification is required and how.
Can You Fix the Site Without Taking Our Booking System Offline?
Often, yes. If the booking engine is hosted by a third party, it usually keeps working while we clean the WordPress side. If bookings run inside WordPress and the infection touches checkout, a short maintenance window is safer than taking payments on a compromised page. We agree on timing with you first.
Our Host Suspended the Account. What Now?
Ask the host for the reason and for temporary access to the files, which most hosts grant for cleanup. Send us that access, and we clean the files and database, then give the host what it needs to lift the suspension. Don’t create a new account and copy the old site into it: the infection travels with it.
Is a Cleanup Different for a WooCommerce Store That Takes Cards?
Yes. We check the checkout page source, payment gateway files, and the database for skimming code first, and we document the timeline in case your payment processor or attorney asks. If card data may have been exposed, contact your processor promptly; they have their own procedures.
How Do We Know the Backdoor Is Really Gone?
We compare core files with clean copies, review every plugin and theme file that changed, check scheduled tasks and admin accounts, and then monitor file changes in the weeks after the cleanup. If something reappears, we treat it as part of the same incident. Hardening the site afterward makes a repeat far less likely.