 0498 70 98 60
Hacked WordPress Site Repair in Denver: Clean Site, Sales Back on Track
A customer emails to say your online store redirected her to a fake sneaker shop. Your Google Ads account flags “malicious software.” Or orders simply stop coming in on a Saturday in ski season. A hacked WordPress site costs sales every hour it stays infected, and the damage to trust lasts longer than the hack itself.
Référenceur provides hacked WordPress repair in Denver for businesses of all sizes, from online stores to B2B suppliers. We remove the malware, find and close the vulnerability, and harden the site so the attack can’t simply repeat. The work is done remotely, with clear updates in English, or in French if your management prefers.
Our team has maintained and repaired WordPress sites for more than 15 years, and Référenceur is rated 4.7/5 across 107 Google reviews. Tell us about the incident: we begin with a free diagnostic call.
You can also run a first check yourself. Enter your domain in the scanner below for a free look at problems visible from outside.
Spot a Hacked Site Before Your Customers Do
Most malware is built to hide from site owners while exploiting your visitors and your rankings. Look out for:
- Redirects to spam or scam sites, sometimes only for mobile users or visitors coming from Google.
- Strange pages indexed under your domain, often in Japanese or advertising pharmaceuticals.
- A Google Safe Browsing warning in Chrome or other browsers.
- Unknown administrator accounts or plugins you didn’t install.
- Payment pages behaving oddly, or customers reporting card fraud after buying from you.
- Your host suspending the site or warning about unusual activity.
- Google Ads or Merchant Center disapprovals for compromised or malicious content.
If you notice any of these, start with our guide on what to do when your WordPress site is hacked.
What a Hack Costs a Front Range Business
The first cost is lost revenue. For an outdoor brand selling online, a hack during a seasonal peak can wipe out weeks of planned sales. For an aerospace supplier, a browser warning can be enough for a buyer to move on. Google Ads suspends ads that point to infected pages, and Merchant Center may pull your products.
Rankings suffer next, and slowly. Customers who search your brand name may see spam titles or a warning next to your listing. Spam pages injected under your domain can stay in Google’s index for weeks, and cleaning them up takes deliberate work in Search Console.
Data is the third concern. Colorado law generally requires notifying affected residents within 30 days after determining that a security breach occurred, and the Attorney General when 500 or more Colorado residents are affected. This isn’t legal advice: your attorney decides, and we provide the technical evidence.
What Our Denver Malware Removal Service Includes
| Area | Our work | What you get |
|---|---|---|
| Analysis | Site code, database tables, access logs, users, and cron jobs | The entry point and the scope of the attack |
| Cleanup | WordPress malware, injected scripts, backdoors, and spam pages removed | A clean site |
| Ecommerce | Checkout flow, payment scripts, and customer accounts checked | Sales that resume safely |
| Updates | PHP, WordPress, theme, and plugins; abandoned plugins replaced | The vulnerability closed |
| Hardening | Credentials reset, two-factor authentication (2FA), reduced permissions, web application firewall (WAF) | A smaller attack surface |
| Search Console, review request, index cleanup, Google Ads and Merchant Center checks | Warnings lifted once Google validates the fix | |
| Monitoring | Integrity checks and alerts | Reinfection spotted early |
Our article on removing malware from WordPress explains the technical stages. The complete service is outlined on our national hacked WordPress site repair page.
Our 4-Step Process
How long it takes depends on the infection and how quickly we get access.
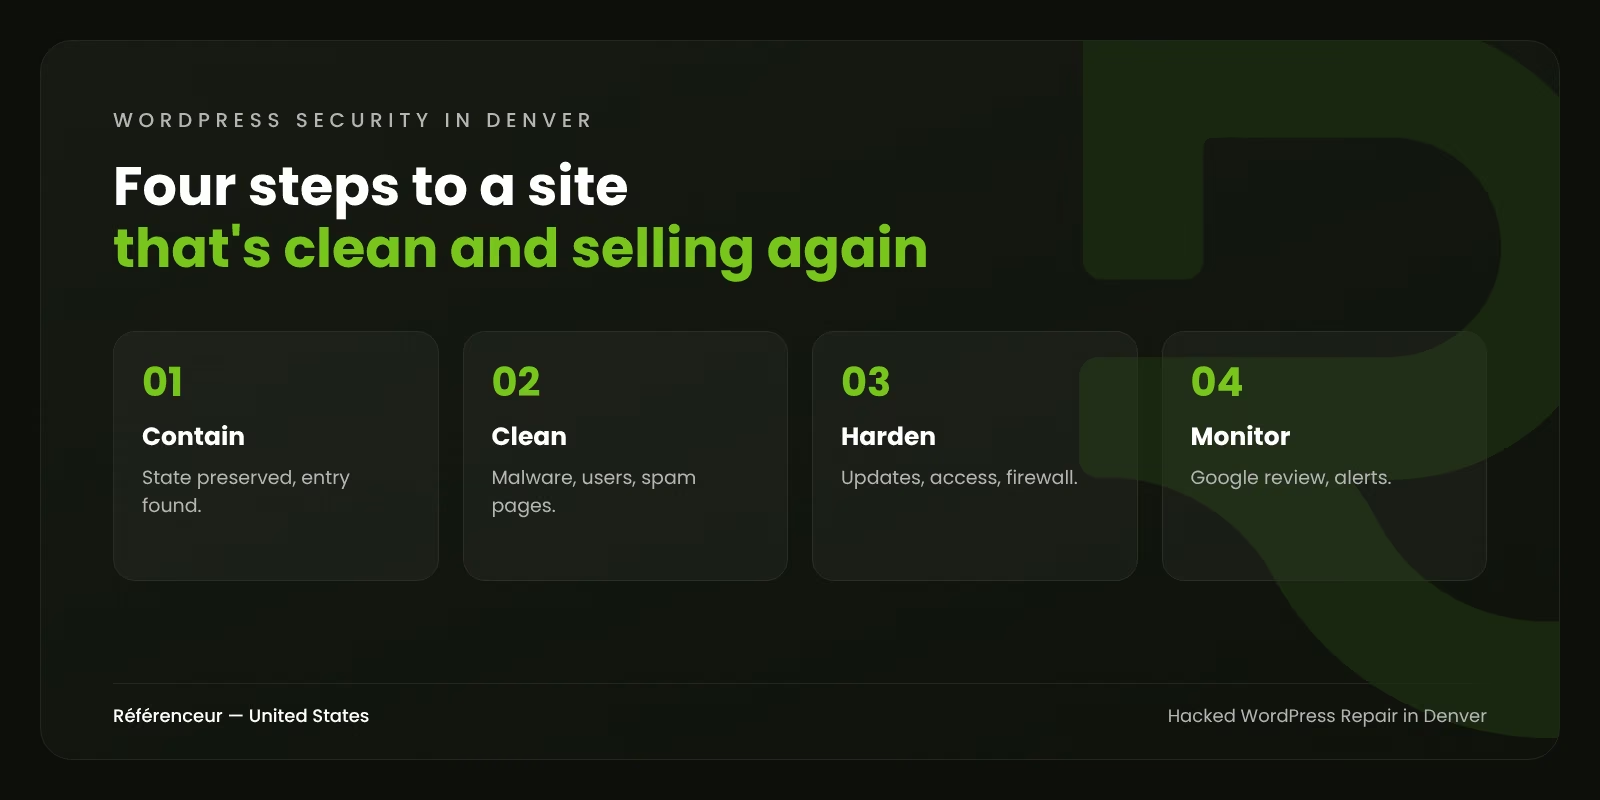
- Contain: current state preserved, damage limited, entry point identified.
- Clean: malicious code, rogue users, and spam content removed from files and database.
- Harden: vulnerability fixed, updates applied, credentials renewed, firewall configured.
- Monitor: Google review requests submitted, alerts set up, incident summary delivered.
Most cleanups take one to several business days once we have access to the site, the hosting account, and any recent backups. Google’s review of a warning may add a few days, which nobody can speed up.
For online stores, we don’t declare the job done until a test order goes through cleanly. We check that payment scripts load only from your provider, that no skimming code remains, and that order confirmation emails reach customers. If card data may have been exposed, we document what we found for your payment processor.
WordPress Security in Denver: Priorities by Business Type
| Business profile | Main risk | Priority |
|---|---|---|
| Outdoor or sports brand selling online | Seasonal sales interrupted | Fast restoration, payment check, Merchant Center |
| Aerospace supplier on the Front Range | Credibility with prime contractors | Full cleanup, shareable incident report |
| Clinic or health practice in Aurora | Sensitive data | Exposure analysis, findings for your legal counsel |
| Services firm in the Denver Tech Center | Contact forms blocked | Forms and email restored, hardening |
| French-speaking association or school | Site run by volunteers | Automatic updates, simpler access, training |
Why Denver Businesses Trust Référenceur With a Hacked Site
Removing the visible symptoms is the easy part, and many quick fixes stop there. Finding how the attacker got in is what prevents a repeat. It’s the step we never skip on a hacked WordPress repair in Denver.
- We trace the entry point instead of just deleting infected files, then close it for good.
- You receive a written report in English or French for your team, insurer, or headquarters.
- The same team can restore ads, recover rankings, and rebuild the site if needed.
- We tell you plainly when rebuilding would be safer than cleaning again.
We have no U.S. office and work from Belgium and Luxembourg. Belgium is typically eight hours ahead of Denver, so our day often starts while you’re still asleep, which helps when an incident hits overnight. The client examples on our case studies page are European.
Stay Protected After the Cleanup
Reinfections usually come through outdated plugins and reused passwords. Our WordPress security guide covers the routines that keep a site safe. If a rebuild makes more sense, our web design agency in Denver can take it on. See all our Denver services on our digital marketing agency in Denver page, and Midwest companies can visit our hacked WordPress repair in Chicago.
Check Your Site’s Security
Not sure whether your site is compromised? Run the free scanner below; it takes a few seconds and needs only your domain:
Request a free assessment of your hacked WordPress site in Denver. We’ll estimate the extent of the infection and the likely entry point, then send a repair plan priced in U.S. dollars. Send us a few lines about what you’re seeing, and we’ll respond as fast as we can, typically the same business day in Central European Time.
Hacked WordPress Repair FAQ for Denver
Should We Restore an Old Backup Right Away?
Not before we look. A backup may already contain the malware, and restoring it erases evidence of the entry point. Change your passwords first, then contact us.
Will Our Google Ads Be Reinstated?
Once the site is clean, we request a review in Google Ads and Search Console. Google usually reinstates ads after verification, but the timing is Google’s decision.
Can You Fix a WooCommerce Store?
Yes. We check the checkout, payment scripts, customer accounts, and order emails, and we coordinate with your payment provider if card data may have been exposed.
Are We Required to Notify Customers?
It depends on the data involved and where affected people live. Colorado has specific notification rules. This isn’t legal advice: we provide the facts, and your attorney decides.
How Do We Prevent the Next Hack?
Keep WordPress, plugins, and PHP current, delete unused plugins, enable 2FA, and keep off-site backups. We offer maintenance with monitoring if you’d rather hand it off.