 0498 70 98 60
Hacked WordPress Site Repair in Burlington, VT: A Clean Site, Then Monitored
A customer from Quebec emails you: your website just sent her to a rigged lottery page. Your booking engine shows strange characters. Google labels your domain as dangerous. These signs almost always mean a hack. For a Burlington business, a compromised site cuts off sales and bookings overnight.
We provide hacked WordPress repair for Burlington VT businesses entirely remotely, with a technician who can work with you in English or in French. That French-speaking WordPress support helps Quebec-owned companies and their head offices follow every step. We remove the infection, fix the vulnerability that let the attacker in, and bring the site back online cleanly. Then we keep watching it to catch any new attempt.
Our team has maintained WordPress sites for more than 15 years. Clients rate us 4.7/5 across 107 Google reviews, and we’re a Google Partner. Get a free assessment with the address of the affected site: the first diagnostic call is free.
Want a quick first reading? Our free scanner checks the security signals visible from outside your site in a few seconds.
Symptoms That Point to a Hacked WordPress Site
Many infections stay hidden from logged-in administrators. They target visitors arriving from Google, from mobile phones, or from specific countries. Watch for these signs:
- Redirects to scam pages, sometimes only for first-time visitors or mobile users.
- Spam pages in other languages showing up in Google under your domain.
- Spam emails sent from your server and your sending address placed on a blocklist.
- A “Deceptive site ahead” warning in Chrome or a security alert in Google Search Console.
- Unknown administrator accounts, odd PHP files in the uploads folder, or a slower site.
- Booking or checkout pages that behave strangely, a sign that payment data may be targeted.
Resist the urge to delete everything. Infected files help identify the entry point, and our page on the first hours after a WordPress hack explains what to preserve.
Why the Stakes Are High for Burlington Businesses
Many local businesses depend on online bookings: inns, restaurants, tour operators, ski and lake rentals. When a site redirects or shows a warning, travelers from Montreal or Boston simply book elsewhere. Lost bookings rarely come back once a competitor has them.
B2B companies face a different risk. Suppliers to GlobalFoundries, the UVM Medical Center, or aerospace firms like Beta Technologies are judged on reliability. An infected website raises questions about your IT practices, even if your internal systems are fine.
Google Ads also stops showing ads that lead to a compromised site, so paid traffic disappears at the same moment.
Personal data brings specific duties. According to a November 2025 memo from Vermont’s Office of Legislative Counsel, a business that suffers a security breach must send a preliminary notice to the Attorney General within 14 business days and notify affected consumers within 45 days. If your customers live in Quebec or other states, other rules may apply. This isn’t legal advice; check with your attorney. We give them a precise, dated technical record.
Our 4-Step Process
Every cleanup follows the same order. How long it takes depends on the extent of the infection.
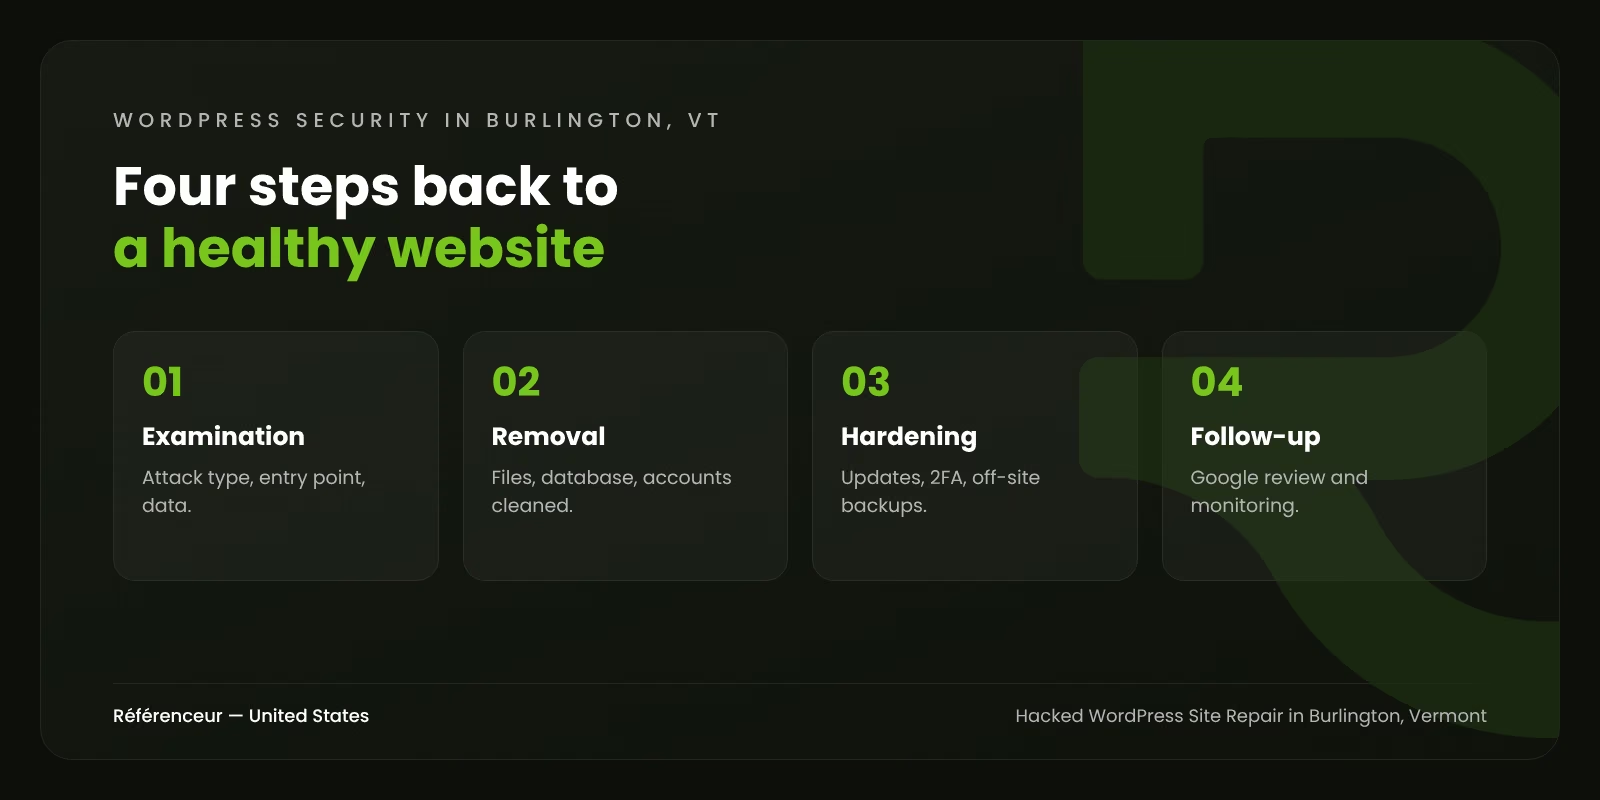
- Examination: a full backup of the infected site, the attack type, the probable entry point, and the data exposed.
- Removal: files, database, and accounts cleaned, usually within a few hours to a few days.
- Hardening: core, theme, plugins, and PHP updated, access secured, and backups moved off the server.
- Follow-up: a Google review request, an indexing check, and close monitoring for several weeks.
Google processes reconsideration requests on its own timeline. We keep monitoring throughout, so a reinfection doesn’t catch you off guard.
What Our Hacked Site Cleanup in Burlington Covers
Removing visible malware is only half the job. We also find out how the attacker got in and close that door. Our guide to WordPress malware removal explains the technical background.
- File cleanup: backdoors, injected code, and unknown files removed from core, theme, and plugins.
- Database cleanup: spam posts, hijacked options, rogue users, and hidden links removed.
- Entry point fixed: outdated plugin, stolen password, or hosting weakness identified and corrected.
- Updates: core software, theme, plugins, and PHP brought up to supported releases.
- Hardening: 2FA, tighter file permissions, a web application firewall (WAF), and unused plugins removed.
- Booking and checkout checks: payment pages and forms reviewed for skimming scripts.
- Google recovery: spam URLs removed from the index and a review requested in Search Console.
- Backups and monitoring: off-site copies, a tested restore, and file change alerts.
You receive an incident report in English, with a French version for your Quebec or European head office if needed.
Different Businesses, Different Priorities
How we handle a hacked WordPress site in Burlington depends on the role your site plays in your business. Five typical cases:
| Company profile | Priority | What we put in place |
|---|---|---|
| Inn or hotel with online booking | Restore bookings quickly | Booking engine checked first, redirects removed, monitoring tightened |
| Online store selling Vermont products | Restart U.S. and Canadian sales | Checkout audit, a search for skimming scripts, and a Google review |
| Quebec subsidiary with a U.S. site | Reassure head office and customers | A bilingual incident report and an access review across both sites |
| Industrial supplier near Essex Junction | Stay credible with large accounts | Documented cleanup, a detailed report, and hardened logins |
| Cross-border services firm | Protect client documents | Review of forms and uploaded files, with facts for counsel |
Why Trust Référenceur With Your Hacked Site
We handle WordPress security alongside our SEO and Google Ads teams. After cleanup, we check what Google shows for your site in both languages, and if your ads were suspended, we follow them through reapproval.
There’s no U.S. office on our side; our technicians are based in Francorchamps, Belgium, and Wemperhardt, Luxembourg. Server work requires access, not proximity, and we ask for temporary credentials that you revoke once we’re done. No site is ever fully immune, and we won’t pretend otherwise; we offer a careful method and transparent follow-up. Our references are European clients such as Isolpur, Lupulus, Menuiserie Rosen, and Auto-école Georges: see our case studies.
Rebuild on Solid Ground
An old site built on abandoned plugins will eventually fall again, even after cleanup. Our web design agency in Burlington can rebuild it properly. The national hacked WordPress site repair page details the full service.
All our local services are on our digital marketing agency in Burlington page. A related company was hit in Massachusetts? Our hacked WordPress repair in Boston page covers it. To get started, tell us what’s happening on your site and request a free assessment.
Still unsure? Run a second check with our free scanner:
FAQ About Hacked WordPress Sites in Burlington, VT
How Quickly Can You Start?
Sites that are down, redirecting, or flagged by Google take priority over routine work. We confirm timing on the first call. Having your hosting, SFTP, and WordPress credentials ready speeds things up, or you can send us the details now.
Will Our Google Rankings Recover?
A long infection can drop pages or trigger a warning in search results. After cleanup and review, rankings often recover gradually, but nobody can promise an identical return.
Do We Have to Notify Our Customers?
Possibly, if their personal data was stored on the site. Rules vary depending on where affected people live: Vermont, another state, or Canada. Consult an attorney quickly; we provide the technical findings.
What Does the Repair Cost?
The price depends on the type of infection, site size, and the number of vulnerabilities to fix. We quote in U.S. dollars after the free assessment, never sight unseen.
How Can We Avoid Another Hack?
Update core, theme, and plugins promptly and delete what you don’t use. Insist on a supported PHP version, unique passwords, and 2FA, and keep tested off-site backups. Our WordPress security guide covers the rest.