 0498 70 98 60
Hacked WordPress Site Repair in Phoenix: Cleaned Up and Taking Inquiries Again
A prospect tells you your website shows a fake virus alert. Your RFQ form hasn’t received a single message in 10 days. Or Google Ads suddenly disapproves every ad. For a Phoenix company, a hacked WordPress site shuts down the main channel for new inquiries.
We work remotely to analyze the attack, clean the site, close the vulnerability, and put it back online. A technician explains each step in plain language, in English or French. Your U.S. team receives a written incident summary in English if needed.
Référenceur has maintained and repaired WordPress sites for more than 15 years, partners with Google and Microsoft Advertising, and holds a 4.7/5 rating across 107 Google reviews. Get a free assessment of the incident before any work begins.
Before you even contact us, you can run a quick check. Our free security scan below reviews your site’s visible protections in seconds.
Warning Signs to Take Seriously
An infection often stays invisible to a logged-in administrator. It shows up for visitors, search engines, or your web host instead. These are the most common symptoms.
- Redirects to casinos, shady pharmacies, or scams, sometimes only on smartphones.
- Japanese-language pages or counterfeit product listings indexed under your domain in Google.
- Email from your domain landing in spam, or your host blocking outgoing mail.
- A red browser warning, or a security issue reported in Google Search Console.
- Unknown admin accounts, changed passwords, or plugins installed without your approval.
- Google Ads disapproved for malicious software.
- Unexplained slowdowns, or unknown PHP files in the uploads folder.
If you see one of these signs, don’t delete files at random. Our guide on what to do when your WordPress site is hacked lists the first moves that preserve evidence.
What a Compromised Site Costs a Phoenix Business
Many Phoenix companies live on inbound requests: industrial RFQs, construction bids, medical appointments. When the site is infected, that flow stops. Visitors don’t warn you; they simply move on to the next supplier.
Search engines react too. Once Google detects malware, it can display a warning before visitors reach your pages, and Google Ads may suspend ads that point to an infected domain. Every day of delay makes recovery longer.
Email is often the hidden casualty. When a hacked site sends spam, mailbox providers start distrusting your domain, and quotes from your sales team land in junk folders. We check your domain’s sending reputation and its SPF, DKIM, and DMARC records as part of the cleanup.
Then there’s personal data. Arizona’s data breach notification law requires notice when certain personal information is compromised, and other states apply their own rules based on where affected people live. We provide the technical findings; your attorney determines the obligations. This isn’t legal advice.
Our 4-Step Process
Acting in the right order avoids destroying evidence or leaving a door open. Timelines depend on the infection and on how quickly we receive hosting access.
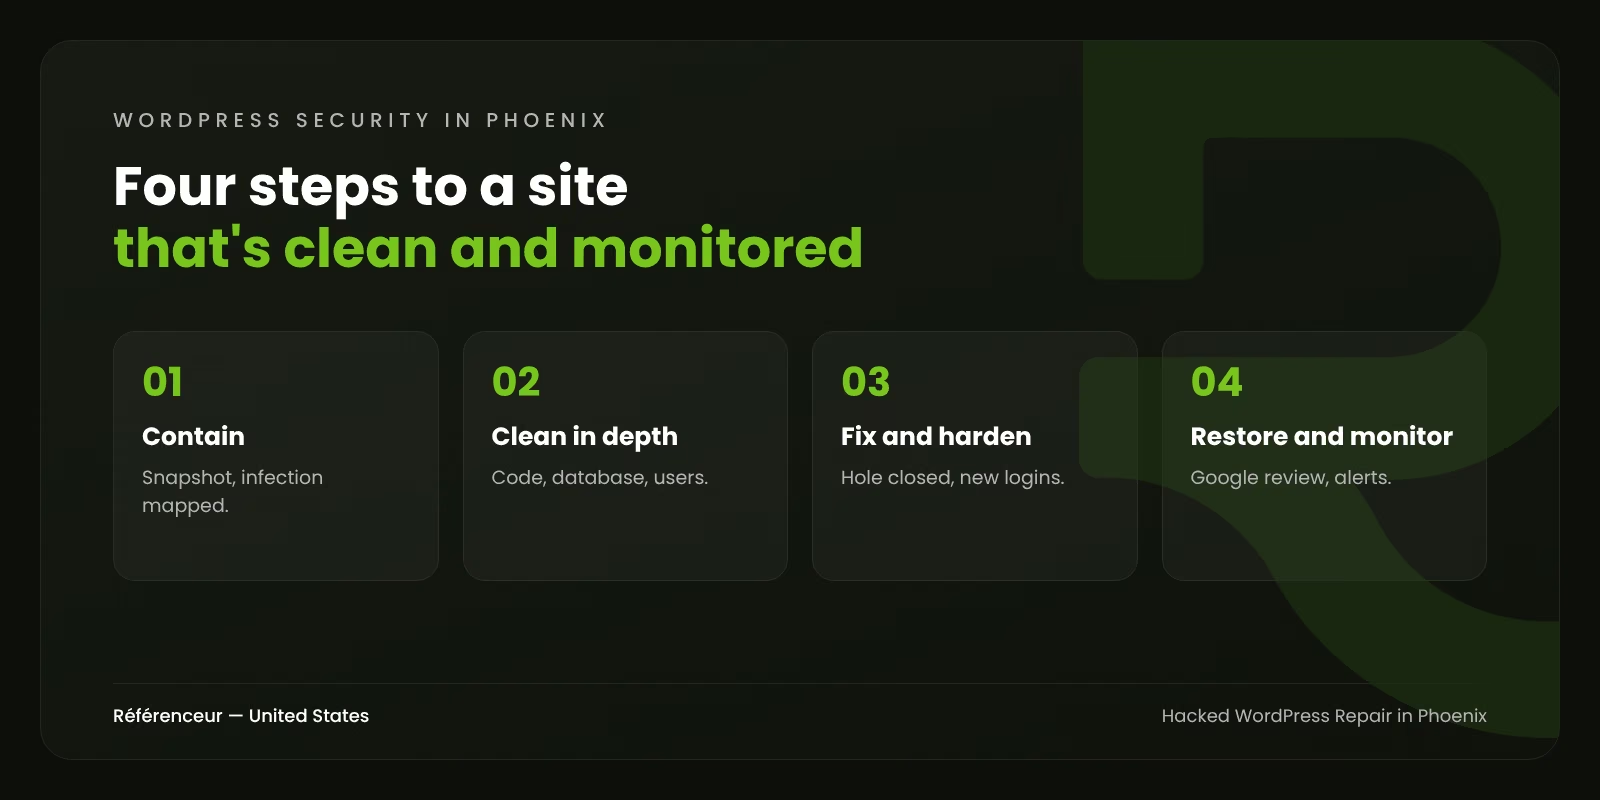
- Contain and diagnose: we snapshot the infected site, map the infection, and check whether personal data was exposed.
- Clean in depth: injected code, polluted database tables, ghost users, and suspicious scheduled tasks.
- Fix and harden: the original vulnerability closed, updates applied, credentials reset, and protections added.
- Restore and monitor: final checks, a Google review request if needed, then ongoing alerts.
You receive a written update at each stage, so you always know what was found and what remains to be done.
What Our Hacked Site Cleanup in Phoenix Covers
A cleanup isn’t an automated scan. Here are the points we handle on every job.
| Area | What we do |
|---|---|
| Files | Malicious code and backdoors removed, WordPress core, theme, and plugins checked against clean versions |
| Database | Injected spam, hidden links, and rogue admin accounts removed |
| Root cause | An outdated plugin, a weak password, an abandoned theme, or a server setting identified and fixed |
| Updates | Core, theme, and plugins updated, PHP moved to a supported version |
| Hardening | Two-factor authentication (2FA), file permissions, login limits, and a web application firewall (WAF) |
| Backups | Automatic off-server backups with a tested restore |
| Spam URLs removed, review requested in Search Console, follow-up until warnings are lifted | |
| Ads | Disapproved ads reviewed and resubmitted once the site is clean |
Removing malware without fixing the cause solves nothing, because the attacker returns through the same opening. Our guide to WordPress malware removal shows why half-finished cleanups don’t last. For the full scope, see our national hacked WordPress site repair service.
Hacked WordPress in Phoenix: From Scottsdale to Chandler, Different Priorities
The priority depends on what the site does for your business. Six situations come up often across the Valley.
| Business profile | Priority | Our response |
|---|---|---|
| Industrial supplier with an RFQ form | Get quote requests flowing again | Form and mail delivery checked first, attachments scanned |
| WooCommerce store in Scottsdale | Reopen sales without exposing customers | Payment scripts checked, cleanup, closer monitoring |
| Real estate agency in Tempe | Remove spam pages showing in Google | Index cleanup, search result checks, access hardening |
| HVAC or solar contractor running Google Ads | Restore suspended campaigns | Landing pages verified, ads resubmitted |
| Healthcare practice with online booking | Protect patient inquiries | Forms and integrations reviewed, logs preserved for counsel |
| French-speaking firm with a bilingual site | Clean both language versions | Every translation and redirect checked |
Why Call Référenceur
Our WordPress security specialists work with our SEO and Google Ads teams. The SEO team watches reindexing; the Google Ads team handles ad reapproval. One contact coordinates everything, which is what sets our hacked WordPress repair in Phoenix apart from a one-off malware scan.
We work from Belgium and Luxembourg, without a U.S. office. Malware cleanup is remote work by nature: all we need is access to your hosting and to wp-admin. Every job ends with a written report covering how the attacker got in, what we removed, which accounts we reset, and what we recommend next. Leadership, your insurer, or your attorney can keep it as a record of the incident. Describe what you’re seeing, even if you’re not sure it’s a hack. Our references are European, including Lupulus, Isolpur, Auto-école Georges, and Menuiserie Rosen; see our case studies. To avoid the next incident, read our WordPress security guide.
After the Cleanup: Build on Solid Ground
An old site full of abandoned plugins stays an easy target even once it’s clean. Our web design agency in Phoenix can rebuild it on a maintained foundation. Every service for the region is on our Phoenix digital marketing agency page. If your group also runs a California site, our hacked WordPress repair in Los Angeles page covers it.
Not sure the site is really infected? Run the free scan again here.
Request a free assessment for hacked WordPress repair in Phoenix by sending us your site’s address. We identify the type of infection, its visible effects in Google, and the access points to secure first.
Hacked WordPress Site FAQ for Phoenix Businesses
How Quickly Can You Start?
We typically begin the diagnostic as soon as your hosting and WordPress admin credentials arrive. The rest depends on how deep the infection goes, and a recent hack is usually fixed faster than an old one.
Should We Take the Site Offline?
Sometimes, briefly, to protect visitors. A maintenance page is often better than serving malware. We advise you during the first call, depending on what the infection does.
Do We Have to Notify Our Customers?
That depends on the data involved and on the laws of the states where affected people live. Our analysis states what was exposed and for how long. Your attorney then decides which notices are required.
How Much Does a Cleanup Cost?
The cost depends on the site’s size, the extent of the infection, and the number of vulnerabilities. We don’t quote without examining the site. You receive a proposal in U.S. dollars after the free diagnostic, before any work begins.
How Do We Prevent It From Happening Again?
Keeping WordPress up to date, enforcing 2FA with strong passwords, and storing backups off the server cut the risk sharply. Monitoring catches problems early, and we can provide that follow-up after the cleanup.