 0498 70 98 60
Hacked WordPress Site Repair in Los Angeles: Fast Cleanup, Lasting Protection
A customer in Santa Monica emails you a screenshot: your homepage sent her to an online casino. The next morning, Google shows “This site may be hacked” under your business name, and your ads get disapproved. Your dashboard looks normal, yet the inquiries have stopped.
A hacked WordPress site can be fixed, but only with a method. We find how the attacker got in, remove the malicious code, close the hole, and harden the site so it is far harder to break into again. You get a clean website back, along with the trust of your customers. That is the standard Los Angeles businesses should expect from hacked WordPress repair.
Référenceur has built, maintained, and repaired WordPress sites for more than 15 years. We are a Google Partner, and our clients give us 4.7/5 across 107 Google reviews. Everything happens remotely, in English or French. Report your compromised site for a free assessment.
Want a quick first read right now? Our free tool below scans your WordPress site for common security issues.
Warning Signs Your WordPress Site Was Hacked
Attackers try to stay hidden as long as possible. Redirects often target only mobile visitors or people arriving from Google, never the logged-in administrator. That’s why you should test your site from a phone in a private window.
- Some visitors land on gambling, fake giveaway, or online pharmacy pages.
- Google indexes pages in Japanese or products you don’t sell, the classic Japanese keyword hack.
- Your emails land in customers’ spam folders, or your host flags mass mailing from your account.
- “This site may be hacked” appears under your listing in search results.
- Google Ads disapproves your ads for a compromised site or malicious software.
- An unknown admin account appears, or PHP files show up in your uploads folder.
Don’t restore an old backup without checking it first. It often contains the backdoor the attacker already planted, and the infection returns a few days later. For the first hour after you notice a hack, follow the checklist in our article WordPress site hacked: what to do.
What Our Hacked WordPress Repair in Los Angeles Covers
Every cleanup follows the same thread: understand, clean, protect, monitor. Here is what that includes, area by area.
| Area | What we do | What you get |
|---|---|---|
| Investigation | File review, access logs, user accounts, and scheduled tasks | The likely point of entry |
| Files | Malware, injected scripts, and backdoors removed | Clean code |
| Database | Spam pages, hidden links, and attacker-created users deleted | Content free of spam |
| Updates | PHP, WordPress core, theme, and plugins updated; abandoned plugins replaced | The vulnerability closed |
| Hardening | New credentials, 2FA, tighter file permissions, request filtering | A much harder target |
| Backups | Off-server copies and a tested restore | Fast recovery if needed |
| Search Console checked, review request filed, index cleaned | The warning removed once Google validates it | |
| Monitoring | Regular checks and alerts on file changes | Early detection of a repeat attack |
Automated scanners miss things. A manual code review always completes their work, especially on older sites. For a technical look at the process, read our article on how to remove malware from WordPress.
Our 4-Step Process
Timelines are estimates. They depend on the infection, the size of the site, and how quickly we get hosting access.
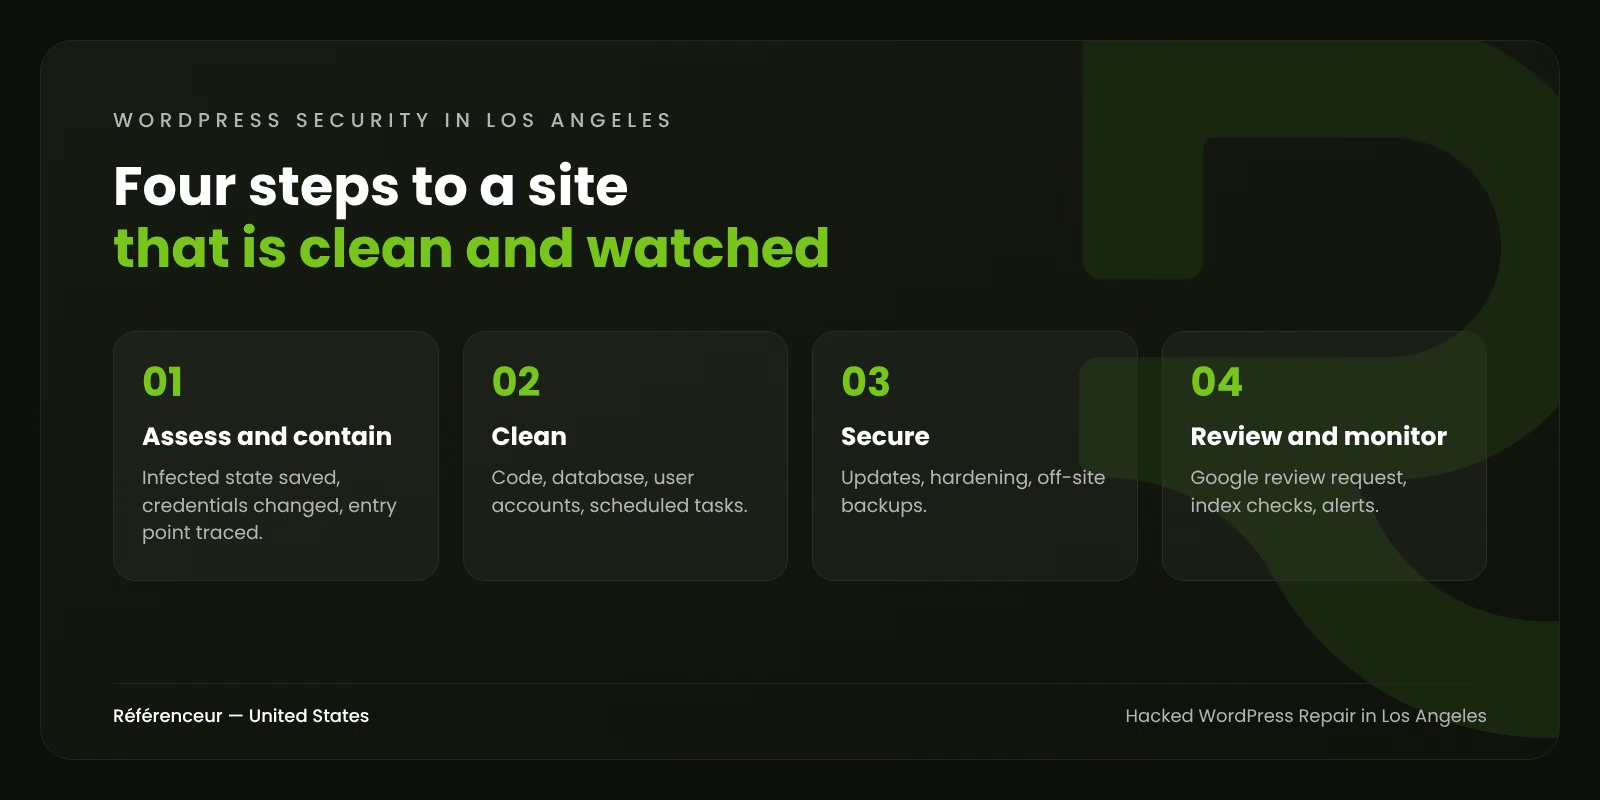
- Assess and contain: snapshot of the infected state, credentials changed, entry point investigated. We start as soon as your hosting login reaches us.
- Clean: code, database content, user accounts, and scheduled tasks. A typical business site is often cleaned in one to two days.
- Secure: updates, hardening, unnecessary plugins removed, off-site backups set up.
- Review and monitor: Google review request, index checks, and alerts on any change.
Removing a Google warning depends on Google, which processes review requests at its own pace. We follow the case until it is closed and keep you informed at each step.
WordPress Security Priorities by Type of Business
A hack doesn’t cost a studio, an online store, or a law firm the same. For each profile, we set a different order of priorities. These profiles are illustrative.
| Business profile | Main risk | What we prioritize |
|---|---|---|
| Fashion or beauty brand selling online from Downtown LA | Payments and customer data | Checkout first, WooCommerce review, access logs |
| Law or advisory firm in Century City | Confidentiality and reputation | Forms and accounts reviewed, written incident report |
| Silicon Beach startup raising a round | Credibility with investors | Fast cleanup, locked-down access, verified Google index |
| Caterer or specialty food shop with online orders | Lost orders | Forms and email checked, off-site backups |
| Local Google Ads advertiser | Suspended ads | Cleanup, Search Console review, ad re-approval follow-up |
Many small companies in the region manage their own WordPress site without a technical team. That’s exactly where regular maintenance pays for itself. Tell us about your site and your hosting, and we’ll assess how well it’s protected.
Why Trust Référenceur With Your Hacked Site
Référenceur has no office in California or anywhere else in the U.S. WordPress malware removal happens on the server, so distance doesn’t slow it down. For hacked WordPress repair, Los Angeles companies need speed and method, not a storefront. You talk directly with the person cleaning your site, by email or video call, in English or French.
Emergencies don’t wait for the next meeting. We start on your credentials as soon as they arrive, and calls can be set early in the morning, Pacific Time. Because our day starts while Los Angeles sleeps, cleanup often moves forward overnight from your point of view. You receive a written incident report you can share with your insurer or attorney.
Data exposure is the question to answer early. California’s SB 446, in effect since January 1, 2026, sets a 30-day deadline to notify affected residents after a breach is discovered. Breaches affecting more than 500 Californians must also be reported to the Attorney General. We document the technical facts; your attorney decides what applies. This isn’t legal advice.
We also run SEO and Google Ads, which matters after an attack: spam pages removed from the index, rankings watched, ads relaunched. No provider can make a site invulnerable, but we sharply reduce the risk. Our published case studies come from European clients such as Isolpur and Menuiserie Rosen. Browse our case studies.
After the Cleanup: Put Your Site Back to Work
If your site is too outdated to secure properly, our Los Angeles web design team can rebuild it on a clean base. For prevention, our WordPress security guide covers the habits that keep attackers out.
Full details of the service are on our national hacked WordPress site repair page. A sister site was hit in Northern California? See our page on hacked WordPress repair in San Francisco. For a broader plan, visit our digital marketing agency in Los Angeles page.
Still unsure whether your site is truly clean after an alert? Our scanner gives you a free first report in moments:
Need help now? Send us the address of the affected site. Your free assessment identifies the type of infection, the likely vulnerability, and the plan to get your site back online.
Hacked WordPress FAQ for Los Angeles Site Owners
How Fast Can You Start?
Usually within the business day after we receive your hosting and WordPress access. The time difference often works for you, since we keep working during your night. A small business site is often back to normal within two days.
Will My Google Rankings Drop?
They can slip if the infection lasts, especially with SEO spam. A fast cleanup limits the damage. We get the spam pages removed from Google’s index and then track your rankings.
How Much Does a Cleanup Cost?
The price depends on the size of the site, how far the infection spread, and the updates needed. We don’t sell a flat package. You receive a precise quote in U.S. dollars after the free assessment, before any work begins.
Can My Site Get Hacked Again After You Fix It?
Yes, no website is ever fully immune. Prompt updates, two-factor authentication, and off-server backups cut the risk considerably. Our maintenance plan keeps those defenses current month after month.
What Can I Do to Prevent Another Intrusion?
Apply security updates as soon as they’re released, from PHP to plugins. Limit the number of administrators and delete unused accounts. Once a quarter, confirm that your backups actually restore.