 0498 70 98 60
WordPress Redirect Hack: How to Expose It and Shut It Down
A WordPress redirect hack quietly sends some of your visitors to an online casino, a fake sweepstakes, or a page asking for their credit card number, while you, sitting at your desk, see a perfectly normal site. That disconnect is expensive: the owner assumes the customer clicked the wrong link, and the customer assumes the business has abandoned its domain.
Référenceur, a European digital marketing agency with offices in Belgium and Luxembourg, helps small businesses, independent professionals, and nonprofits reproduce the redirect, trace it to its source, and restore the site, entirely remotely. This guide explains why this kind of hack slips past site admins, how to prove it yourself, and where the malicious code usually hides.
Check your WordPress site’s security: run a free initial scan right now with the tool below.
This article builds on our complete WordPress security guide and our page on the warning signs of a hacked WordPress site. You can also run a free security scan of your domain right here on this page.
When Your WordPress Site Redirects to Another Site Only for Some Visitors
If your WordPress site is redirecting to another site only some of the time, it’s almost never a bug. The injected code picks its targets carefully so the site owner doesn’t notice, sometimes for months.
The usual filters are the traffic source (a click from Google or a social network), the device type (smartphones only), and the absence of a WordPress login cookie, which tells the script the visitor isn’t logged in. Some scripts fire only once per person, which makes the problem much harder to reproduce.
Google classifies this behavior as sneaky redirects in its spam policies and notes that hacked code can redirect users based on referrer, user agent, or device. Search Console even has a dedicated manual action for sneaky mobile redirects.
How to Reproduce the Redirect Step by Step
Before you go hunting for code, you need to prove the problem in a way you can repeat. For every test, write down the time, device, browser, page language, and landing URL. Those details point you straight to the right place to look.
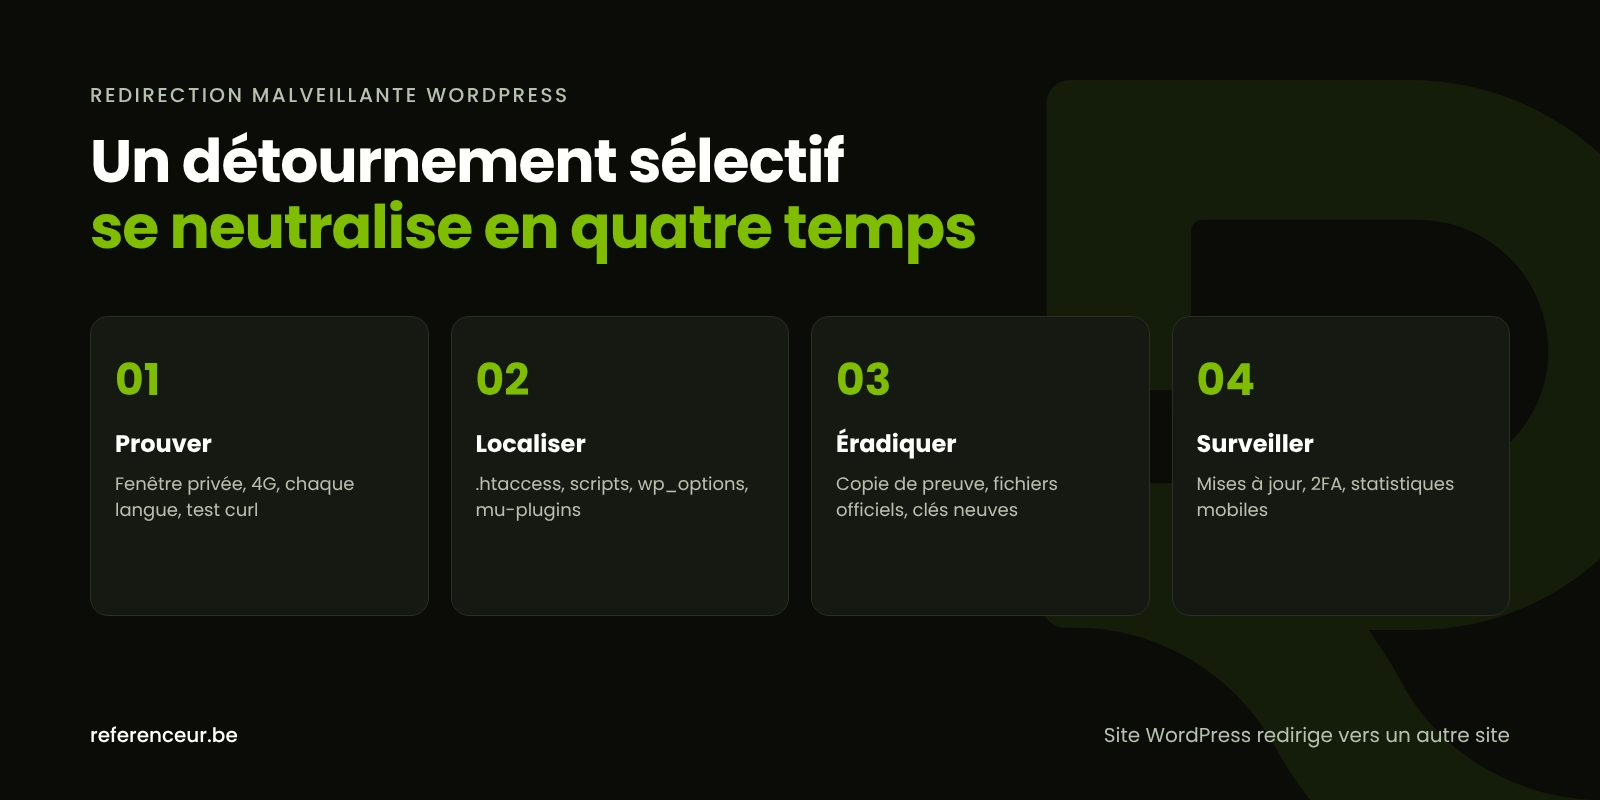
- Private browsing window on a desktop, logged out of WordPress: first type your URL directly, then reach the site through a Google search.
- Smartphone on cellular data (4G or 5G), off your office Wi-Fi, clicking your site in the search results.
- Every language version of the site (English, Spanish, or any other), because the script may target only one.
- URL Inspection in Search Console: the live test shows the page exactly as Googlebot receives it.
- Google Transparency Report, to check whether Safe Browsing is already flagging your domain.
curl -sI -A "Mozilla/5.0 (Linux; Android 14; Pixel 8)" -e "https://www.google.com/" https://www.yourdomain.com/This command simulates a phone arriving from Google and returns only the HTTP headers. A Location line pointing to an unfamiliar domain gives away a server-side redirect. A JavaScript redirect, on the other hand, only shows up in the full page source or in your browser’s developer tools.
Where a WordPress Redirect Hack Hides
A single WordPress redirect hack is often triggered from several places at once, which is why so many cleanups fail. Here are the hiding spots to check, every time.
| Location | Telltale Sign | How to Check |
|---|---|---|
| .htaccess files | A RewriteCond on HTTP_REFERER or HTTP_USER_AGENT followed by a rule pointing to a third-party domain | Search every .htaccess file for these variables, subfolders included |
| Injected scripts | Obfuscated JavaScript in the header, footer, or a theme .js file | Read the page source served in a private window |
| wp_options table | Altered siteurl or home values, or an option that loads an external script | Review the options and the settings of any code snippet plugins |
| Content and widgets | A script tag slipped into a post, a page, or a Custom HTML block | Search wp_posts and widgets for script tags |
| Plugins, mu-plugins, theme | A PHP file that checks the visitor’s device or traffic source | WP-CLI checksums and a comparison with the original theme |
grep -rn -e "HTTP_REFERER" -e "HTTP_USER_AGENT" --include=".htaccess" .
wp option get siteurl
wp option get home
Run from the site root, the first line lists every suspicious condition in each .htaccess file. The two WP-CLI commands display the URLs WordPress uses, which must match your domain exactly, protocol included.
Remove the Code and Keep It From Coming Back
Start with a full copy of your files and database, stored off the server, so you keep evidence and have a way back. Don’t restore an old backup until you know when the problem started: it may already contain the script.
Replace every compromised .htaccess file with the “Basic WP” block from the WordPress documentation, adding back only the rules you understand. Remove any scripts slipped into content, widgets, and options, then reinstall WordPress core, your plugins, and your theme from their official sources.
Next, find the point of entry: PHP files in wp-content/uploads, unknown admin accounts, suspicious cron jobs. Our WordPress malware removal process walks through these checks, and regenerating your security keys logs out any sessions that are still open.
Finally, rerun the same tests you started with, on the same devices. A redirect that comes back a few hours later almost always points to a scheduled task or a forgotten file that rewrites the code.
Updates, Backups, and Traffic Monitoring
Most of these hacks exploit an outdated plugin, theme, or PHP version. Apply updates to every component and check your PHP version with our article on WordPress security and PHP versions.
Tighten access with two-factor authentication, unique passwords, and the removal of accounts belonging to former vendors. Schedule off-server WordPress backups and verify them with an actual test restore. If Google or browsers display a warning, our page on a WordPress site blocklisted by Google explains how to request a review.
Last, keep an eye on your analytics: a sudden drop in mobile sessions, or in time on page for landing pages reached from Google, can reveal a redirect before any customer reports it. A properly configured web analytics setup doubles as an alarm system.
Remote Diagnosis and Cleanup Over Video Call
A redirect is actually best diagnosed remotely, since you need to see the site the way an outside visitor does. A video kickoff call lets us reproduce the problem together over a shared screen and gather the access we need.
We then track down and remove the code using temporary credentials that are revoked as soon as the work is done. You receive a report listing every location we cleaned and the likely vulnerability, along with a short recorded training session so you can run the tests yourself.
After that, a monthly check-in can keep updates and backups on track. As a European agency, we work with U.S. businesses remotely, through video calls, shared screens, and monthly reporting. Our hacked WordPress site repair page covers the full service.
WordPress Redirect Hack: Your Questions Answered
Why Does the Redirect Only Affect Smartphones?
Many scripts read the user agent and target only mobile devices, which account for more traffic and get checked less often by site admins. Test on cellular data, off your office Wi-Fi, and arrive through a Google search. This behavior is typical of a WordPress redirect hack lodged in the .htaccess file or in an injected script.
My WordPress Site Redirects to Another Site Only When Visitors Come From Google. Is It Hacked?
Almost certainly. When a WordPress site redirects to another site only for visitors coming from Google, code is checking the referrer to hide from the owner. Your customers could land on a scam, and Google may display a warning or issue a manual action. Treat it as a break-in, not a misconfigured setting.
Could a Redirect Manager Plugin Be the Cause?
Yes, in two ways. A compromised admin account may have added rules to a legitimate plugin, so review every redirect it contains. A vulnerable plugin may also have served as the point of entry. Either way, check the rules, update or replace the plugin, and then review your list of admin accounts.
Will Switching Themes Make the Problem Go Away?
Rarely. The code often lives in the .htaccess file, the database, a plugin, or a must-use plugin, all of which stay active no matter which theme you use. Switching themes can even mask the symptom temporarily and make it look fixed. It’s better to pinpoint the exact source, then reinstall the original theme from its developer.
My Hosting Provider Says the Server Is Clean. Who Should I Turn To?
The server can be clean while your WordPress installation isn’t, because your host monitors the infrastructure, not your files. Send them your documented tests and ask for the access logs. If the redirect leads to fraud, you can also report it to the FBI’s Internet Crime Complaint Center (IC3) or to CISA. All of this evidence makes an intermittent WordPress redirect hack much easier to track down.
Should I Notify Customers Who Were Redirected?
If the landing page asked for login credentials, a payment, or a download, give your customers a calm heads-up and advise them to change any passwords they entered. The FTC’s consumer guidance on phishing and identity theft can help them. If personal information processed by your site was exposed, state data breach notification laws may require you to notify affected individuals and, in some states, regulators; get advice from a qualified attorney.
Not sure your site is clean? Run a free security scan of your WordPress site:
Are some visitors landing on a site you don’t recognize? Book a short video call: we’ll reproduce the redirect with you over a shared screen and map out a plan to remove it for good.