 0498 70 98 60
Hacked WordPress Site Repair in Philadelphia: Cleaned Up, Trust Restored
A hospital purchasing team tries to open your website and gets blocked by its security gateway. A university lab reports the same thing the next day. Nobody tells you why; they simply stop responding. For suppliers in Greater Philadelphia, a flagged domain can quietly cut you off from your best customers.
Référenceur repairs hacked WordPress sites for Philadelphia-area businesses. We work remotely to remove the infection, close the vulnerability, lift browser and search warnings, and get your forms, ads, and reputation back on track. Updates come in clear English, or in French for teams reporting to a European or Quebec parent company.
We have maintained and repaired WordPress sites for more than 15 years and have a 4.7/5 rating across 107 Google reviews. Get a free assessment of the incident, and we’ll tell you right away what to do first.
Want a quick first check? Our free scanner below looks for signs of compromise that are visible from outside your website.
How to Recognize an Infected WordPress Site
Attackers mostly exploit plugins and themes that haven’t been updated. These are the traces they leave most often:
- Redirects to gambling, pharmacy, or scam sites, sometimes only for visitors coming from Google or using a phone.
- Thousands of spam URLs indexed under your domain, often in Japanese.
- Warnings from Chrome, Safari, or a corporate firewall, or a security issue flagged in Search Console.
- Google Ads disapproved for malware, or the ad account suspended.
- Your domain on an email blocklist because the server is sending spam.
- Unknown administrators, recent PHP files in upload folders, or plugins nobody installed.
Large organizations in the region filter the sites their staff can visit. Hospitals, universities, and industrial groups use security gateways that block domains flagged as dangerous, often without telling anyone. WordPress security in Philadelphia directly affects your access to those customers.
Some sites are more exposed than others. Websites for medical practices, labs, and healthcare providers tend to stack plugins for appointment booking, detailed forms, and document libraries, each with its own update cycle. Every plugin adds attack surface, especially if its developer has stopped maintaining it. Multilingual sites sometimes run overlapping translation plugins as well. A precise inventory of those components is part of every diagnosis.
Dealing with an infection right now? Our guide on what to do when your WordPress site is hacked lists the first steps. Our national hacked WordPress site repair page describes the infections we handle.
What Our Cleanup Includes
Each hacked WordPress repair in Philadelphia covers the full chain, from diagnosis to monitoring:
- Diagnosis: infection type, probable date of compromise, the vulnerability exploited, and the extent of the damage.
- File cleanup: WordPress core, theme, plugins, uploads, and hidden files anywhere on the server.
- Database cleanup: injected scripts, spam content, rogue users, and malicious options or scheduled tasks.
- Backdoor removal, so attackers can’t simply walk back in.
- Closing the hole: updates to PHP, WordPress, theme, and plugins, or replacement of abandoned components.
- Hardening: new credentials everywhere, two-factor authentication, file permissions, and a web application firewall.
- Reputation recovery: a review request to Google, checks against blocklists, and a request to re-review your Google Ads account.
- Tested off-site backups and monitoring to catch any reinfection.
We work with the access you provide, typically your hosting control panel, a WordPress admin login, and Search Console. Dedicated accounts are created for the job and removed afterward. The technical side of the work is explained in our WordPress malware removal guide. No cleanup can make a site immune to attack, but an updated, monitored, backed-up site is far harder to compromise.
Our 4-Step Process
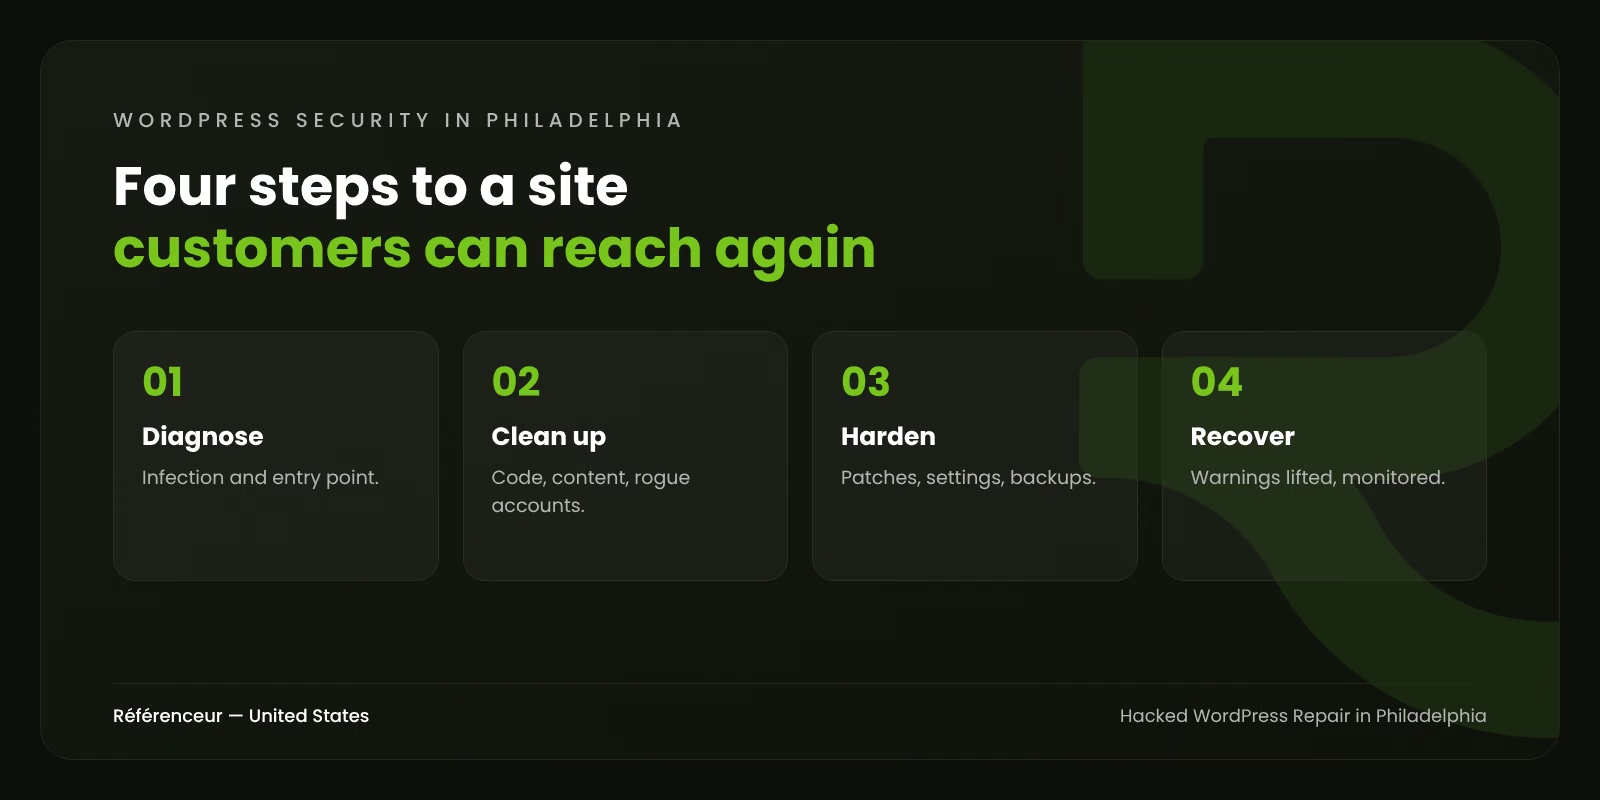
- Emergency diagnosis: the infection and probable entry point identified, with a quote before any billable work. We usually deliver it within one working day on European time.
- Cleanup: malicious code, injected content, and rogue accounts removed, working on a copy first whenever we can.
- Hardening: patched software, stricter settings, and fresh backups, so the same entry point can’t be reused.
- Recovery and monitoring: warnings lifted, forms tested, ads reinstated, and monitoring over the following weeks.
First-Hour Mistakes That Make Recovery Harder
When a site is compromised, the instinct is to act fast. Some quick reactions, though, make the cleanup longer and more expensive:
- Restoring last month’s backup without finding the entry point, which usually leads to reinfection within days.
- Deleting the hosting account or reinstalling WordPress on top of infected files, which destroys useful evidence.
- Changing only the WordPress password while hosting, SFTP, and database credentials stay the same.
- Emailing customers a link to the site before warnings are lifted.
If you’re unsure what to do, talk to us before changing anything. A short call often saves days of work.
Hacked WordPress Repair in Philadelphia: Priorities by Business Profile
| Business profile | Main risk | Our priority |
|---|---|---|
| Lab or biotech supplier | Domain blocked by hospital and university filters | Complete cleanup, warnings lifted, reputation lists checked |
| Manufacturer along the Route 202 corridor | Lost quote requests | Forms back online fast, outgoing email verified |
| Law or consulting firm in Center City | Confidential documents and messages exposed | Attachments, forms, and accounts reviewed |
| WooCommerce store of a French brand | Payment data and customer accounts | Checkout flow, accounts, and payment plugins checked |
| French-language association or media outlet | Site hijacked to send spam | Cleanup, account security, and domain reputation |
Already had a repair and want to confirm the site is clean? Run another scan below.
Why Work With Référenceur
- A clear explanation of the incident, in English or French, that you can share with headquarters or customers.
- A full cleanup of files and database, documented in a written report.
- Marketing checks once the site is clean: rankings, ads, analytics, and forms.
- Practical prevention advice sized to your team and budget, starting with our WordPress security guide.
Our references are European companies such as Lupulus, Menuiserie Rosen, Auto-école Georges, and Isolpur, covered in our case studies. If the site needs rebuilding, our web design agency in Philadelphia takes over. For the full range of what we do in the region, visit our digital marketing agency in Philadelphia page. If your group also runs a website for a New York office, our hacked WordPress repair in New York page covers it.
Request your free hacked-site assessment for Philadelphia: an analysis of the infection, the likely entry point, and a precise quote. Sites that are down are handled first.
Philadelphia Hacked WordPress FAQ
How Fast Can You Start Working on Our Site?
Emergencies come first, typically within the next business day, Central European Time. Belgium is usually six hours ahead of Philadelphia, and we confirm timing in our first exchange.
Why Can Hospitals or Universities Still Not Reach Our Site After the Cleanup?
Their security gateways often rely on reputation lists that update on their own schedule, sometimes days after Google has cleared your site. We request reviews where possible and check major blocklists. Sometimes a short message to your contact’s IT team speeds things up.
Do We Have to Notify Anyone If Personal Data Was Exposed?
Pennsylvania’s Breach of Personal Information Notification Act, updated in 2024, sets notification rules, and New Jersey and Delaware have their own breach laws. Which ones apply depends on where affected people live. We document what happened for your counsel. This isn’t legal advice: your attorney decides what notifications are required.
What Does a WordPress Cleanup Cost?
It depends on the scope of the infection, the size of the site, and the hardening required. The free assessment comes first; a quote in U.S. dollars follows, and nothing is charged until you accept it.
How Can We Prevent Another Infection?
Regular updates, fewer plugins, named accounts with two-factor authentication, and tested backups. Remove accounts belonging to former staff or contractors as soon as they leave. Ongoing monitoring completes the picture, and we can handle that maintenance for you.