 0498 70 98 60
Hacked WordPress Site Repair in Austin: Fast Cleanup, Sales Back on Track
Your sales team is preparing an important demo. That morning, the prospect writes: when they opened your website, their browser warned of a security risk. In tech, a compromised site casts doubt on your entire technical credibility.
A hacked WordPress site in Austin also means lost form submissions, suspended Google Ads, and sometimes exposed customer data. Référenceur works remotely to clean the site, remove backdoors, fix the vulnerability, and restore your sales channel. You get updates at every step, in English or in French for teams that report to a European or Quebec parent company.
We have repaired and secured WordPress sites for more than 15 years and are rated 4.7/5 across 107 Google reviews. Request a free assessment of the incident: we start with a no-cost diagnostic and tell you the first steps to take.
For an immediate first check, use our free scanner. It looks for anomalies detectable from outside, such as suspicious scripts or redirects.
Symptoms of a Compromised WordPress Site
Most attacks exploit known flaws in plugins or themes that weren’t updated. The most common signs:
- Redirects to fraudulent sites, sometimes only for visitors coming from Google or on mobile.
- Spam pages indexed under your domain, often in Japanese or pushing counterfeit products.
- A warning in Chrome or Safari, or a security issue notice in Google Search Console.
- Google Ads disapproved for malware, sometimes with the account suspended.
- A host suspending your site for mass email sending or abnormal resource use.
- Unknown administrators, unusual PHP files, or plugins nobody remembers installing.
Some signals are subtler. A sudden traffic spike from countries you don’t sell to can reveal an infection. So can a site that slows down for no reason, or inquiries that drop off a cliff. Google Search Console sometimes flags the problem before you notice anything on screen. Our guide on what to do when your WordPress site is hacked walks through the first checks.
For an Austin company, the impact goes beyond a marketing site. Prospects, partners, and sometimes investors check your website before every meeting. WordPress security in Austin is tied directly to commercial trust.
The underlying cause is usually mundane. Most WordPress compromises we investigate start with an outdated plugin, a reused password, or an old admin account belonging to someone who left. Attackers don’t target you personally; automated tools scan thousands of sites for the same known holes and exploit whatever they find. That’s why a quick fix without closing the entry point so often leads to a second infection a few weeks later.
Fast-growing companies are especially exposed. Their site was often built quickly at launch, then extended with plugins added campaign after campaign. Nobody really owns maintenance. Our national hacked WordPress site repair page describes the cases we handle.
Our 4-Step Process
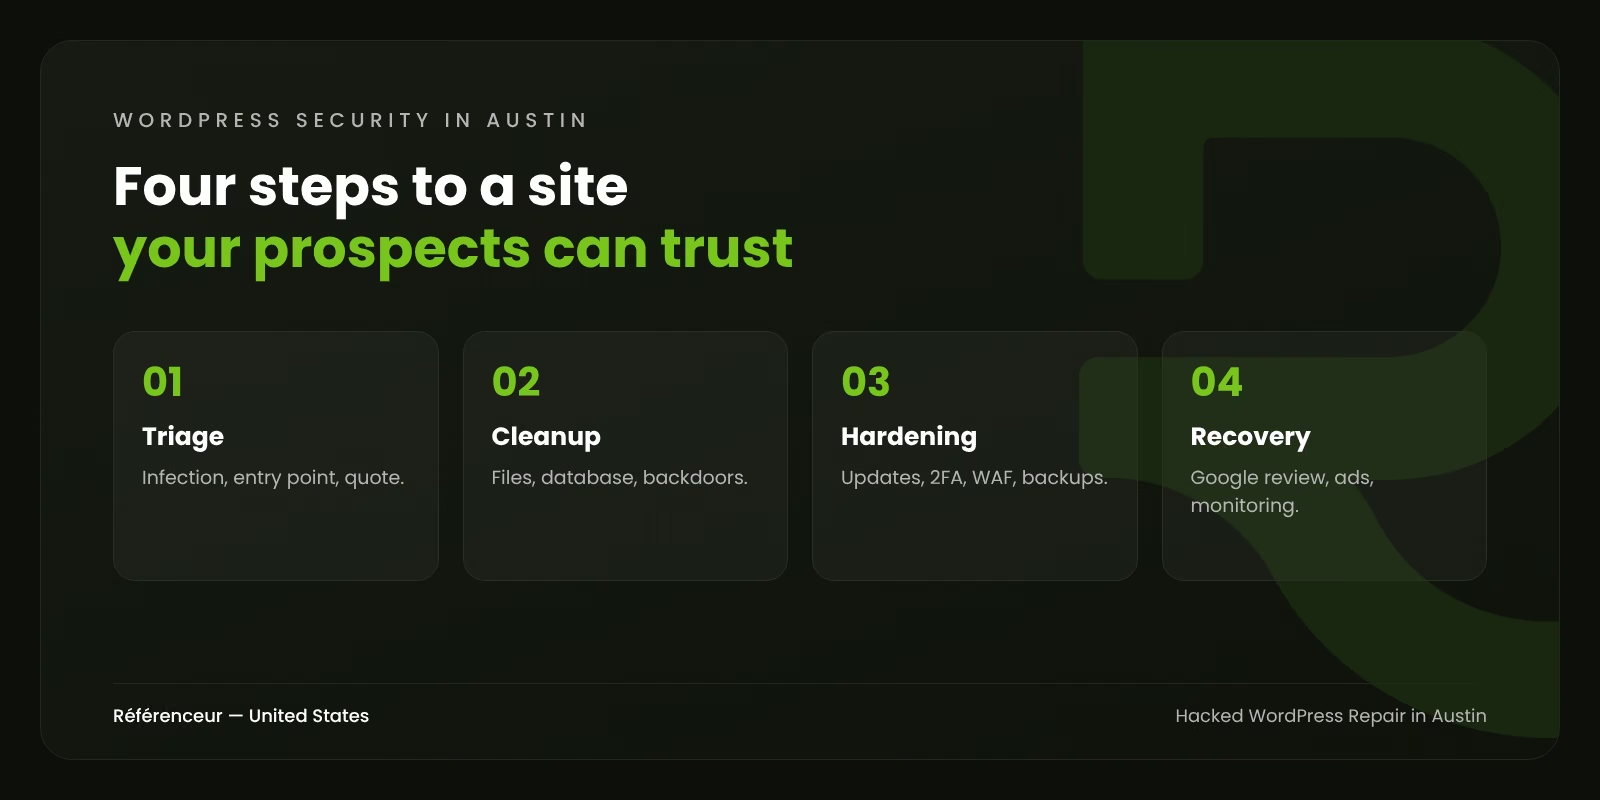
- Triage: we identify the infection, its likely entry point, and its spread, then send a quote before any billable work. This typically takes one business day (Central European Time).
- Cleanup: files, database, users, and scheduled tasks cleaned, with backdoors removed.
- Hardening: updates, new credentials, 2FA, a WAF, and tested off-site backups.
- Recovery: Google review request, forms and tracking tested, ads reinstated, and monitoring for reinfection.
What the Cleanup Includes
Every hacked WordPress repair in Austin runs through the same checklist:
- A full scan of WordPress core, themes, plugins, uploads, and server files, compared with clean reference versions.
- Database review: injected scripts, spam posts, rogue admin users, and malicious options.
- Removal of backdoors and web shells, the hidden doors that let attackers return.
- Patch or replacement of the vulnerable plugin or theme, and updates to WordPress and PHP.
- Password resets for WordPress, hosting, SFTP, and the database, plus two-factor authentication.
- Cleanup of spam URLs from Google’s index and a review request through Search Console.
- A written incident report you can share with customers, partners, or investors.
The technical side of the job is detailed in our WordPress malware removal guide. No cleanup makes a site invulnerable, but regular updates, monitoring, and backups cut the risk sharply.
Mistakes to Avoid in the First Hours
- Restoring an old backup without closing the hole: the infection usually returns within days.
- Wiping the server, which erases the logs needed to understand the attack.
- Leaving former contractors’ accounts active “just in case.”
- Assuming that because the homepage looks normal, the site is clean.
- Posting about the incident publicly before you know what data, if any, was affected.
If you have any doubt, reach out before you touch anything. A short call often prevents the kind of rushed fix that turns a one-day cleanup into a week-long recovery.
Hacked WordPress Repair in Austin: The Stakes Depend on Your Business
| Business profile | Main risk | Our priority |
|---|---|---|
| Software company with a WordPress marketing site | Credibility damage before a demo or funding round | Fast cleanup and a clear incident report for customers and investors |
| French brand’s WooCommerce store | Compromised payments and customer accounts | Checkout flow, accounts, and payment plugins reviewed |
| Consultancy working with Texas state agencies | Confidential exchanges exposed | Forms, uploaded files, and access logs analyzed |
| Service business running Google Ads | Blocked ads and lost leads | Cleanup, Google review, and an ad account re-review request |
| Startup whose site was built quickly by a freelancer | Outdated plugins and unknown logins | Access inventory, updates, and replacement of fragile components |
Want to confirm the site is clean after a repair? Run a second scan here.
Once the site is clean, we recommend a light maintenance routine: monthly updates, weekly off-site backups, uptime and file-change monitoring, and a quarterly review of user accounts. We can run it for you, or hand your team a checklist and the access structure to do it in-house.
Why Work With Référenceur
- Clear explanations in English or French that you can forward to leadership.
- A complete cleanup, not a cosmetic one, documented in writing.
- Marketing checks after the fix: rankings, ads, analytics, and forms. For prevention, start with our WordPress security guide.
Our references are European clients, including Lupulus, Menuiserie Rosen, Auto-école Georges, and Isolpur, in our case studies. If the site needs a rebuild, our web design agency in Austin can take over. For everything we do locally, see our digital marketing agency in Austin. Running a site in Houston too? See hacked WordPress repair in Houston.
Request your free hacked-site diagnostic for Austin: the infection analyzed, the likely entry point identified, and a precise quote. Sites that are offline are handled first.
Austin Hacked WordPress FAQ
Should We Take the Site Offline Immediately?
Not always. If visitors are being redirected or payment data is at risk, a temporary maintenance page is wise. Otherwise, keeping the site up while we work avoids losing traffic. We advise case by case in our first conversation.
How Long Does a Cleanup Take?
Most cleanups are completed within a few business days, depending on the size of the site and how deep the infection runs. Google’s review of a security warning can add some time after that. We keep you posted daily, so your sales team knows when it’s safe to send prospects back to the site.
Do We Have to Notify Our Customers?
Possibly. Texas sets notification rules for breaches of sensitive personal information in chapter 521 of its Business and Commerce Code, and other states’ laws can apply depending on where customers live. We document the incident; this isn’t legal advice, so your attorney should confirm your obligations.
What Does a Repair Cost?
It depends on the infection, the size of the site, and the hardening needed. You receive a quote in U.S. dollars after the free diagnostic, before any billable work starts.
Will the Hack Hurt Our Search Rankings?
It can, particularly if spam pages were indexed or Google displays a warning. A fast cleanup and review request limit the damage. We then remove spam URLs, check that your important pages are indexed correctly, and monitor recovery in Search Console over the following weeks.