 0498 70 98 60
Hacked WordPress Site Repair in Seattle: Clean Site, Inquiries Back
Your sales rep forwards an email from a prospect in Bellevue: “Your website just redirected me to a pharmacy store.” Or Search Console sends an alert about hacked content. For a company that relies on its site for quote requests, every hour of infection chips away at trust you spent years building.
Référenceur offers hacked WordPress repair in Seattle for businesses of every size. We remove the malware, find and close the entry point, and harden the site so the same attack doesn’t work twice. All of it is handled remotely, with updates in clear English, or in French if your leadership or parent company prefers.
Our team has maintained and repaired WordPress sites for more than 15 years, and clients give Référenceur 4.7/5 across 107 Google reviews. Tell us what you’re seeing on your site: each case starts with a free diagnostic call.
Want a first look right now? Type your domain into the scanner below for a free check of the problems visible from the outside.
What a Compromised Site Reveals, and Why It’s Spotted So Late
Most infections are designed to stay hidden from the site owner. Attackers want your server and your search rankings, not your attention. The signs often show up for visitors and search engines first:
- Redirects to spam, gambling, or fake shopping sites, sometimes only on mobile or only from Google results.
- Japanese or pharmaceutical pages appearing in Google under your domain.
- A red “Deceptive site ahead” or similar browser warning from Google Safe Browsing.
- Admin accounts you didn’t create, or users whose roles changed overnight.
- A sudden slowdown, unusual server load, or a hosting provider suspending your account.
- Contact forms that stop delivering, or your domain landing on email blocklists.
- Google Ads disapproving your ads for “compromised site” or malicious software.
If you need a practical first-response checklist, read our guide on what to do when your WordPress site is hacked.
The Real Cost of a Hack for a Seattle Business
The direct cost is lost inquiries. For a B2B supplier in Kent or a software company in Redmond, the site is where procurement teams verify you; a browser warning can quietly remove you from a shortlist. Paid traffic stops too, because Google Ads suspends ads that point to compromised pages.
Then comes data. If your site stores customer details, account logins, or form submissions, a breach may trigger legal duties. Washington’s data breach notification law generally requires notifying affected residents within 30 days of discovery, and the Attorney General when more than 500 Washington residents are affected. Health-related data may also fall under the My Health My Data Act. This isn’t legal advice; check with your attorney, and we’ll supply the technical findings they need.
What Our Seattle Malware Removal Service Includes
Each cleanup is adapted to your site, but the work generally covers these steps:
| Area | Our work | What you get back |
|---|---|---|
| Analysis | Files, database, server logs, user accounts, scheduled tasks | The likely entry point and the extent of the infection |
| Removal | WordPress malware, injected scripts, backdoors, spam pages | Clean code and clean content |
| Updates | PHP version, WordPress core, theme, plugins; abandoned plugins replaced | The exploited hole closed |
| Hardening | Passwords and keys reset, 2FA, reduced permissions, web application firewall (WAF) | A smaller attack surface |
| Backups | Off-site copies and a tested restore | A way back if something goes wrong |
| Search Console, review request, spam URL cleanup, Google Ads check | Warnings lifted once Google completes its review | |
| Monitoring | File integrity checks and alerts | A reinfection caught early |
For the technical background, our article on how to remove malware from WordPress explains each stage. You’ll find the complete scope on our national hacked WordPress site repair page.
Our 4-Step Process
The timeline depends on how deep the infection goes and how quickly we get access.
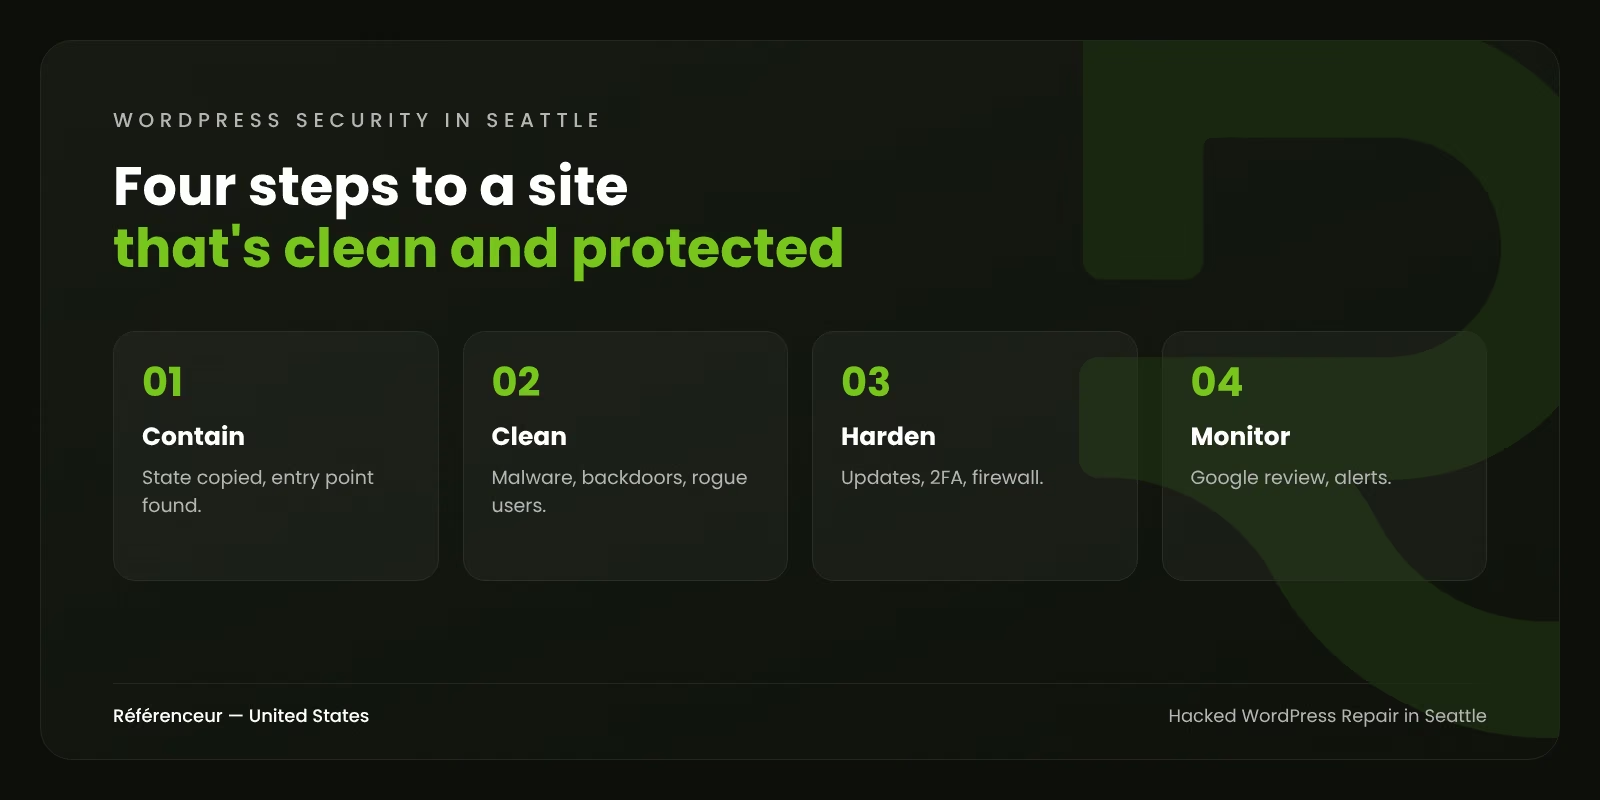
- Contain: we take a copy of the current state, limit the damage, and identify how the attacker likely got in.
- Clean: malicious code, rogue accounts, and spam content removed from files and database.
- Harden: the vulnerability closed, updates applied, credentials renewed, and a firewall configured.
- Monitor: Google review requests submitted, alerts in place, and a short incident report delivered.
A typical cleanup often takes one to several business days once we have access. Google’s review of a security warning can take additional days, and that part is outside anyone’s control.
WordPress Security in Seattle: Priorities by Business Type
The urgent fix differs from one company to the next. Here is where we usually start.
| Business profile | Main risk | Priority |
|---|---|---|
| Online store selling French products | Payments and sales interrupted | Fast restoration, checkout and payment scripts verified |
| Clinic or health practice in King County | Sensitive patient data | Exposure analysis, technical findings for your counsel |
| Software company in Bellevue or Redmond | Reputation with demanding customers | Complete cleanup, incident report you can share |
| Aerospace supplier around Everett | Quote forms blocked | Forms and email delivery restored, hardening |
| French-speaking association or school | Site run by volunteers | Automated updates, simplified accounts, short training |
Why Trust Référenceur With a Hacked Site in Seattle
Speed matters, but so does finding the root cause. A quick cleanup that leaves the backdoor in place usually means a second infection within weeks. That principle guides our hacked WordPress repair in Seattle.
- We look for the entry point, not just the visible symptoms.
- You get a written summary in English or French, suitable for your IT team or headquarters.
- The same team can rebuild trust with Google, restore your ads, and check your SEO.
- We tell you plainly if a full rebuild would be safer than another cleanup.
We have no office in the U.S.; the work is done from Belgium and Luxembourg. Belgium is typically nine hours ahead of Seattle, which means our working day often starts while yours is ending: useful when an incident hits overnight. The client examples on our case studies page come from Europe.
Keep the Site Clean Afterward
Most reinfections come from outdated plugins and weak passwords. Our WordPress security guide lists the habits that prevent the next incident. If the site needs a full rebuild, our web design agency in Seattle can handle it. All our local services are on the digital marketing agency in Seattle page, and California companies can see our hacked WordPress repair in San Francisco.
Run a Free Check on Your Site
Not sure whether your site is infected? Enter your domain below and see what the scanner picks up:
Get a free assessment of your hacked WordPress site. We’ll estimate how far the infection goes and how the attacker likely entered, then send a repair plan priced in U.S. dollars. Send us a short description of the symptoms and we’ll reply as quickly as we can, typically the same business day in Central European Time.
Hacked WordPress Repair FAQ for Seattle
Should We Take the Site Offline Right Away?
Not always. A maintenance page can protect visitors, but deleting files destroys the evidence we need to find the entry point. Change your passwords, then contact us before making major changes.
Will Google Remove the Warning After the Cleanup?
Once the site is clean, we submit a review request in Search Console. Google decides when to lift the warning; it usually happens within days, but we can’t control its timing.
Can You Fix a Site Built by Another Agency?
Yes. We work on most WordPress setups, themes, and hosting providers. We only need admin access, hosting or SFTP access, and ideally your most recent backup.
Do We Have to Notify Customers About the Hack?
It depends on what data was exposed and where your customers live. Washington law sets notification rules for personal information. This isn’t legal advice: we provide the technical facts, and your attorney decides.
How Do We Prevent Another Infection?
Keep WordPress, plugins, and PHP up to date, remove unused plugins, enable 2FA, and keep off-site backups. We can handle this through ongoing maintenance with monitoring.