 0498 70 98 60
Hacked WordPress Site Repair in Washington, D.C.: Clean Site, Leads Restored
Visitors land on a casino site, Chrome displays a red warning, or Google indexes Japanese pages under your domain? Your WordPress site has most likely been hacked. For a business in the D.C. area, every day of infection costs leads and chips away at client trust.
Our hacked WordPress site repair in Washington, D.C., is done remotely. We clean the site, close the vulnerability that was exploited, and bring it back online in a healthy state. You talk with the same technician throughout the job, in English or French. No site is invulnerable, but a well-maintained one defends itself far better.
Repairing and maintaining WordPress sites has been part of our work for more than 15 years. The agency shows 4.7/5 across its 107 Google reviews and works with Google and Microsoft Advertising as a partner. Get a free assessment today.
Before reaching out, try a quick test: our free tool below checks the visible security of your WordPress site in moments.
Signs of a Compromised WordPress Site
An infection often hides from the logged-in administrator, because attackers target visitors arriving from Google or from mobile devices. These are the most frequent symptoms.
- Suspicious redirects to gambling, pharmacy, or scam sites, sometimes on mobile only.
- Japanese SEO spam: thousands of Japanese-language pages appear in Google under your domain name.
- Outgoing spam: your server sends bulk email and your legitimate messages land in junk folders.
- Google warnings: a red screen in Chrome or a security issue alert in Search Console.
- Unknown administrator accounts that nobody on your team remembers creating.
- Google Ads disapproved for malicious software even though nothing changed in your account.
Don’t delete anything in a rush. Some files help trace the entry point, and a hasty restore can reinstall the backdoor. Our guide on what to do when your WordPress site is hacked walks through the first hour.
What a Hack Costs a DMV Business
In the Washington region, the site of a consulting firm or contractor often serves as its business card for demanding buyers. A buyer who sees a security warning won’t fill out your form; they’ll turn to the next competitor without telling you.
Advertising stops, too. Google Ads rejects ads that lead to a compromised site, so if your leads depend on paid search, the flow stops the same day.
On the SEO side, Google may drop infected pages or flag the danger in its results. The longer the infection lasts, the slower the recovery, and a quick response generally limits the losses.
Personal data is the other issue. The District, Maryland, and Virginia each have their own data breach notification law, and conditions and deadlines vary with where affected people live. Your attorney will determine your obligations; we provide the technical facts to inform that review. This isn’t legal advice.
Our Cleanup, Area by Area
A cleanup that leaves the vulnerability open only holds for a few days. We treat the infection and its cause.
| Area | What we do |
|---|---|
| Diagnosis | Review of the file system, database tables, server logs, and every user account |
| File cleanup | Injected scripts and hidden backdoors stripped from WordPress core, the theme, and each plugin |
| Database cleanup | Tables screened for infected posts, altered options, hidden links, and attacker-created users |
| Closing the hole | The plugin, password, or server access that was exploited identified and fixed |
| Updates | WordPress, theme, plugins, and PHP brought to maintained versions |
| Hardening | New passwords, 2FA, file permissions, a web application firewall |
| Backups | Automatic off-server backups with a tested restore |
| Google and Search Console | Removal requests for spam URLs, then a review request when the cleanup is complete |
| Monitoring | Regular comparison of files with their clean version, alerts at the first change |
You’ll receive a written report covering the likely entry point, the actions taken, and our recommendations. It can be shared with your insurer or legal counsel. Our article on WordPress malware removal explains each step in more detail, and the complete offer is on our hacked WordPress site repair page.
Our 4-Step Process
Cleaning up before understanding the attack means it may well come back. We always follow the same sequence, with a duration that depends on the infection.
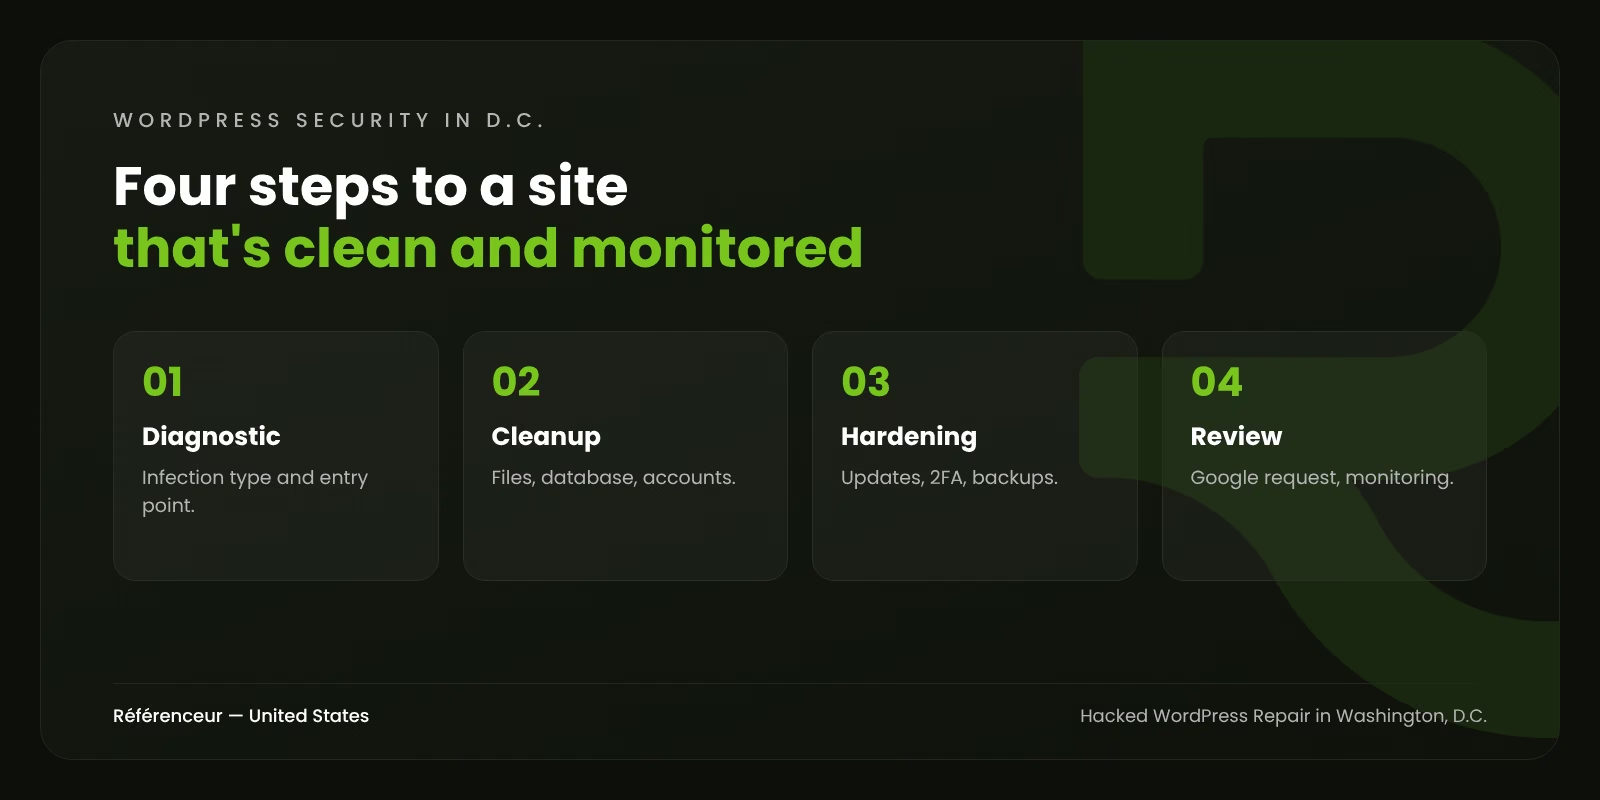
- Diagnosis: we identify the infection type, the likely entry point, and exposed data, and switch the site to maintenance mode if needed.
- Cleanup: files, database, and accounts are sanitized, which can take a few hours to a few days depending on the infection.
- Hardening: PHP, WordPress, and plugin updates, secured access, external backups.
- Review and follow-up: a Google review request, indexing checks, and monitoring in the weeks that follow.
Google processes review requests on its own schedule, which we don’t control. It can take a few days or longer, and we keep an eye on the site for reinfection while we wait.
Hacked WordPress Repair in Washington, D.C.: From NGOs to Online Stores
The urgency isn’t the same for everyone. It depends on the role your site plays in your business. Here are six typical cases in the D.C. area.
| Business profile | Goal | What we put in place |
|---|---|---|
| Contractor serving federal agencies in Reston or Tysons | Reassure clients about its security practices | Documented cleanup, detailed incident report, hardened access |
| Law firm in downtown D.C. | Protect the confidentiality of client communications | Audit of forms and accounts, factual input for the legal analysis |
| Importer of European products selling on WooCommerce | Resume orders without exposing customers | Checkout inspection, search for skimming scripts, priority cleanup |
| NGO or association with a donation form | Keep donor trust | Donation pages verified, redirects removed, tighter monitoring |
| Relocation agency serving expats | Remove spam pages prospects can see | Index cleanup, review request, checks on English and French results |
| European subsidiary running several brand sites | Secure its whole WordPress fleet | Inventory of installs, shared update schedule, alerts on one dashboard |
If you pursue defense contracts, your systems’ cybersecurity is subject to specific requirements. Your public website is only one part of that, but a visible infection makes a poor impression on a prime contractor.
Why Work With Référenceur
Our WordPress security team works alongside our SEO and Google Ads specialists. After the cleanup, we check what Google really sees of your site and follow the recovery. If your ads were suspended, our paid search team follows their reapproval, so you don’t have to coordinate several vendors.
One technician handles your case from first message to final report. We work fully remotely from Francorchamps and Wemperhardt, with no U.S. office; physical presence wouldn’t speed up work that happens on a server anyway. Our references are European clients, including Lupulus, Isolpur, Menuiserie Rosen, and Auto-école Georges: see our case studies.
After the Cleanup: Rebuild and Prevent
An old site with abandoned plugins stays fragile even after cleanup. Our web design agency in Washington, D.C. can rebuild it on maintained foundations, and our WordPress security guide covers prevention. For every service in the region, visit our digital marketing agency in Washington, D.C. page. Is a sister company in New York affected? Our page on hacked WordPress repair in New York applies directly. In any case, describe the symptoms you’ve seen for fast support.
Still not sure your site is actually affected? Run our free security scan:
Request a free assessment by sending us the affected site’s address. We’ll identify the infection type, its visible effect in Google, and the access points to secure first.
Frequently Asked Questions About Hacked WordPress Sites in Washington, D.C.
How Quickly Can You Step In?
Urgent requests get priority, depending on our workload at the time, and we give you a specific timeline in our first exchange. Gathering your hosting, SFTP, and WordPress logins in advance is the single biggest time saver.
Will Our SEO Suffer?
A lasting infection can push pages down or trigger a Google warning. After cleanup and review, rankings generally return gradually, but we can’t promise you’ll get back exactly where you were.
Customer Data May Have Been Exposed. What Should We Do?
Breach notice rules depend on each affected person’s state of residence. Consult an attorney quickly to assess your obligations, and we’ll share the technical findings: affected files, exposure period, and accessible data.
How Much Does a Hacked Site Cleanup Cost?
It depends on the extent of the infection, the size of the site, and the number of vulnerabilities. We don’t sell blind flat fees. You receive a quote in U.S. dollars after the free assessment, before any work starts.
How Do We Avoid Another Hack?
Keep WordPress, your theme, and plugins up to date, and remove what you don’t use. Use a maintained PHP version, unique passwords, and 2FA. Tested backups and monitoring complete the protection.