 0498 70 98 60
Hacked WordPress Site Repair in New York: Clean, Restored, and Secured
This morning, your homepage redirects to a counterfeit store. Or Chrome shows a red warning screen, or your hosting provider just suspended the account. For a company selling in New York, every hour offline costs inquiries, and sometimes the trust of an important client.
A hacked WordPress site calls for a method, not panic. We find the entry point, clean the files and the database, and close the vulnerabilities that let the attacker in. You get back a clean site, restored quickly and much harder to compromise again.
Référenceur has worked on WordPress for more than 15 years and holds a 4.7/5 rating across 107 Google reviews. We can talk you through the incident in English or French while we work. Get a free assessment of the incident: we gauge the extent of the damage before any work begins.
Before you even write to us, you can run a first check. Our free tool, just below, scans your WordPress site’s visible security in a few moments.
Signs of a Compromised WordPress Site and What They Cost You
A hack often goes unnoticed for weeks. These are the symptoms we see most often on business websites.
- Unwanted redirects: mobile visitors in particular land on gambling, online pharmacy, or scam sites.
- Japanese or pharma SEO spam: thousands of unknown pages appear in Google under your domain name.
- Mass email sending: your server sends spam, and your own sales emails end up in junk folders.
- Security warnings: the browser flags your site as dangerous, or Search Console reports a security issue.
- Unknown admin accounts, suspicious PHP files, a sudden slowdown, or a suspension notice from your host.
The damage goes beyond technology. Google Ads can disapprove ads whose landing page is compromised, which cuts off your campaigns overnight. Indexed spam pages also dilute your organic rankings, sometimes for months. For a step-by-step triage, read our guide on what to do when your WordPress site is hacked.
There’s a legal dimension, too. New York’s SHIELD Act applies to businesses that hold private information about New York residents and requires reasonable safeguards. When a breach occurs, the Attorney General’s guidance describes notifying affected individuals and several state agencies. Financial firms supervised by the state’s Department of Financial Services also face their own cybersecurity rules. This isn’t legal advice; check with your attorney.
What Our New York Hacked Site Cleanup Includes
We handle the incident from start to finish. The exact scope is confirmed after the diagnosis.
| Step | What we do |
|---|---|
| Diagnosis | Review of code, database tables, access logs, and the user list |
| File cleanup | Removal of malicious code and backdoors, checks on WordPress core, theme, and plugins |
| Database cleanup | Removal of injected spam, hidden links, and rogue admin accounts |
| Closing the hole | Finding the cause: an unpatched plugin, weak credentials, an abandoned theme, or a misconfigured server |
| Updates | WordPress core, theme, and plugins updated, PHP moved to a supported version |
| Hardening | Two-factor authentication (2FA), file permissions, login attempt limits, a web application firewall (WAF) |
| Backups | Automatic off-server backups, with a tested restore |
| Google review | Spam URLs removed, a review request in Search Console, follow-up until the warning is lifted |
| Monitoring | Regular checks for modified files and an alert at the first anomaly |
Removing malware without treating the cause solves nothing. The attacker comes back through the same door, often within days. That’s why every job includes a root-cause search. Our WordPress malware removal guide explains why partial cleanups fail.
No website connected to the internet is untouchable. Serious WordPress security lowers the risk sharply and shortens your reaction time. The full service is described on our hacked WordPress site repair page.
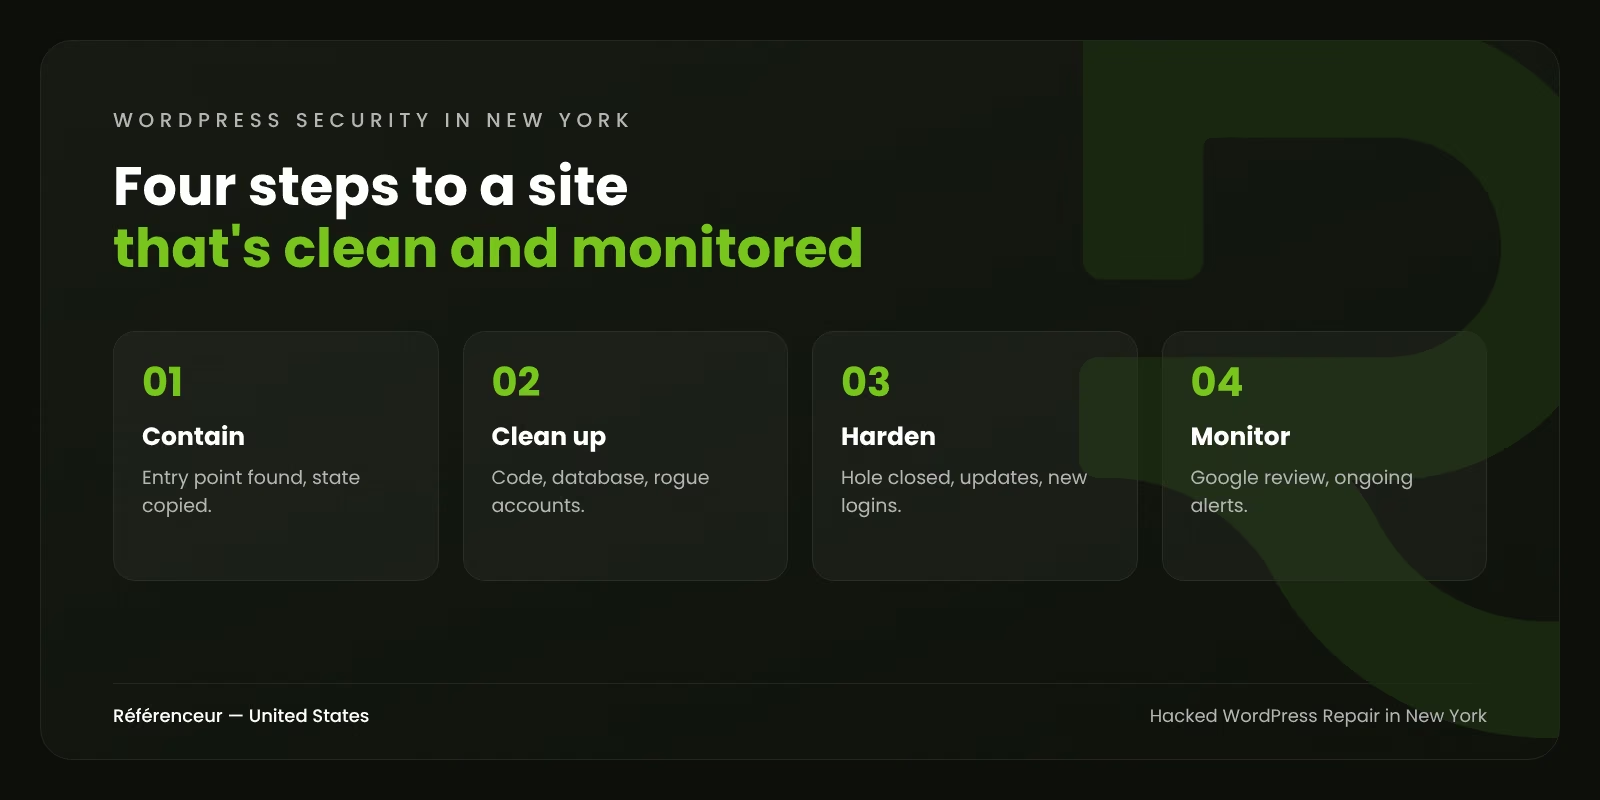
Our 4-Step Process
During an incident, acting in the right order avoids destroying evidence or leaving a door open. Timelines vary with the scope of the infection and how quickly we get hosting access.
- Containment and diagnosis: a copy of the compromised state, analysis of the infection, and a check for exposed data. This starts as soon as we receive your access.
- Deep cleanup: injected code, polluted database tables, ghost users, and suspicious cron jobs. For a typical business site, plan on one to several business days.
- Fix and harden: the original vulnerability closed, updates applied, every credential reset, protections added.
- Back online and monitored: final checks, a Google review request if needed, then alert monitoring.
You get a written update at each step, so you know what was found, what was fixed, and what still needs watching.
Hacked WordPress Repair in New York: Different Businesses, Different Emergencies
Priorities differ from one business to the next, but time works against all of them. Here are situations common among companies in the New York area.
| Business profile | Main risk | Our priority |
|---|---|---|
| Online store selling imported wine, cosmetics, or specialty food | Blocked sales, payment data to protect | Fast restoration, checks on checkout and customer accounts |
| Asset manager or broker regulated by the state | Specific cybersecurity rules and short deadlines | A precise incident report, coordination with your compliance officer |
| Law firm in Midtown | Confidentiality and reputation | Review of forms, attachments, and site-connected mailboxes |
| Startup whose site feeds Google Ads campaigns | Suspended campaigns | Cleanup, ad disapprovals resolved, landing pages verified |
| Cultural organization or association with a members area | Compromised member accounts | Access resets, permission review, member communication support |
| Relocation agency serving expats | Contact forms that stopped sending | Email delivery restored, domain reputation repaired, spam cleaned up |
We always fix what blocks revenue first: sales, inquiries, or campaigns. The full security upgrade follows right after.
Why Trust Référenceur With Your Hacked Site
We don’t just put out the fire. WordPress security sits in the same team as SEO and Google Ads, so we also handle the aftermath: fraudulent URLs to deindex, rankings to rebuild, and ads to get reapproved.
Our specialists work from Belgium and Luxembourg, without an office in the U.S. This kind of job is done remotely anyway, with your hosting and admin access. The time difference can even help: work can move forward while New York sleeps.
One project lead follows the incident from the first message to the final written report. That report covers the cause, the fixes, and our recommendations, and it’s useful for your leadership, your insurer, or your counsel.
Lupulus, Menuiserie Rosen, Auto-école Georges, and Isolpur are among the European clients we work with. See our case studies, then describe what you’re seeing for a first evaluation. To prevent the next incident, our WordPress security guide lists the habits that matter most.
After the Cleanup: Put Your Site Back to Work
A very old site stays fragile even after cleanup. Our web design agency in New York can rebuild it on a maintained foundation. If the hack hurt your rankings, our New York SEO agency speeds up recovery. All our services in the city are on our digital marketing agency in New York page. If a sister office is affected, we also handle hacked WordPress repair in Boston.
Still unsure whether your site is really infected? Run our free security scan below.
Need help now? Request a free assessment for your hacked WordPress site in New York. You’ll learn how far the infection spread, its most likely source, and a plan of action quoted in U.S. dollars.
Frequently Asked Questions About Hacked WordPress Sites in New York
How Fast Can You Start?
The diagnosis starts as soon as we receive hosting and WordPress admin access. What follows depends mostly on how deep the infection goes. A recent hack is usually fixed much faster than one that has been running for months.
Will We Lose Our Google Rankings?
If the infection lasts, Google may demote your pages, especially when thousands of spam URLs have been indexed. The faster you act, the smaller the losses. We remove the fraudulent URLs and monitor recovery, but we can’t promise an immediate return.
Do We Need to Notify Our Customers?
That depends on the data involved and on where the affected people live. In New York, the SHIELD Act governs notification, and other states have their own rules. Our diagnosis documents the incident, but only your attorney can advise you on your obligations.
Isn’t Restoring an Old Backup Enough?
Sometimes, but rarely on its own. Last week’s backup may already contain the malicious code, and the vulnerability stays open. We check any backup before putting it back in place.
How Do We Prevent Another Hack?
Regular updates, strong passwords with 2FA, and off-site backups reduce the risk considerably. Ongoing monitoring catches anomalies early, and we can provide that follow-up after the cleanup.