 0498 70 98 60
Hacked WordPress Site Repair in New Orleans: Fast, Thorough Cleanup
Your site suddenly shows online pharmacy pages in Google. A customer emails to say they were redirected to a fake giveaway. Your web host threatens to suspend the account. Every hour counts, but rushing often makes things worse.
A hacked WordPress site costs New Orleans businesses leads first: hijacked forms, disapproved Google Ads, and a damaged reputation with partners. Référenceur provides hacked WordPress repair for New Orleans companies remotely. We identify the infection, clean the site, close the security hole, and restore your visibility, with clear updates in English, or in French for European headquarters.
Maintaining and repairing WordPress sites has been part of our daily work for more than 15 years, and our clients rate us 4.7/5 on average across 107 Google reviews. Contact us for a free diagnostic call: we assess the situation before any quote.
You can also start with a quick check. Enter your site’s address in our scanning tool below: it looks for several signs of compromise visible online, at no cost.
What a Hack Puts at Stake for New Orleans Businesses
Cybersecurity doesn’t depend on the city. The impact of an intrusion, however, depends heavily on your business and your customers. Typical cases in the region:
| Business profile | Main risk | Our priority |
|---|---|---|
| Freight forwarder or shipping agent tied to the port | Fake quote forms, fraudulent emails sent in your name | Cleanup, form checks, sending domain reputation review |
| Subsidiary of a European group in Jefferson Parish | Incident escalated to headquarters and industrial customers | Fast response and a written report, in English and French if needed |
| Clinic or medical practice tied to a large hospital network | Confidentiality of appointment requests | Audit of forms and uploaded files, stronger access controls |
| Online store of a francophone brand | Blocked orders, exposed payment data | Checkout and payment plugin review |
| School, association, or French-language organization | Family and student data | Cleanup, backups, named accounts, and staff training |
Warning Signs to Watch For
Some infections stay invisible to administrators and only show up through side effects. Watch for:
- Google results with titles unrelated to your business, in Japanese or in spammy English.
- Visitors redirected to other sites, often only on smartphones or only from Google.
- A “dangerous site” alert in the browser, or a message in Search Console.
- Google Ads disapproved for malicious software.
- Undelivered emails because your domain landed on a spam blocklist.
- Admin users nobody recognizes, or plugins that appeared for no reason.
For a business in the region, the first signal often comes from a partner. A European customer reports a suspicious link; an American buyer wonders about an odd email sent from your domain. Those reports are valuable: write down the date, the device used, and the page involved before you contact us. Our article on the first steps after a WordPress hack explains what to do while you wait.
The repair itself works the same anywhere, but your constraints are local: American customers, a European head office, and French-speaking partners. Our incident report is written so you can share it with each of them.
These cases and how we handle them are also described on our national hacked WordPress site repair page.
First Moves While You Wait for Us
A few steps limit the damage before cleanup begins. Change your hosting, WordPress, and FTP passwords from a clean computer. Ask your web host for the date of its last clean server backup, but don’t restore anything yet: restoring an infected copy just brings the problem back. Pause Google Ads campaigns pointing to affected pages. Then hold off on installing new plugins or editing files, which can erase the traces we use to find how the attacker got in.
If your business handles customer accounts or payments, also note who has had admin access in recent months. That list often points straight to the weak spot: an old contractor login, a shared password, or a forgotten test account.
Our 4-Step Process
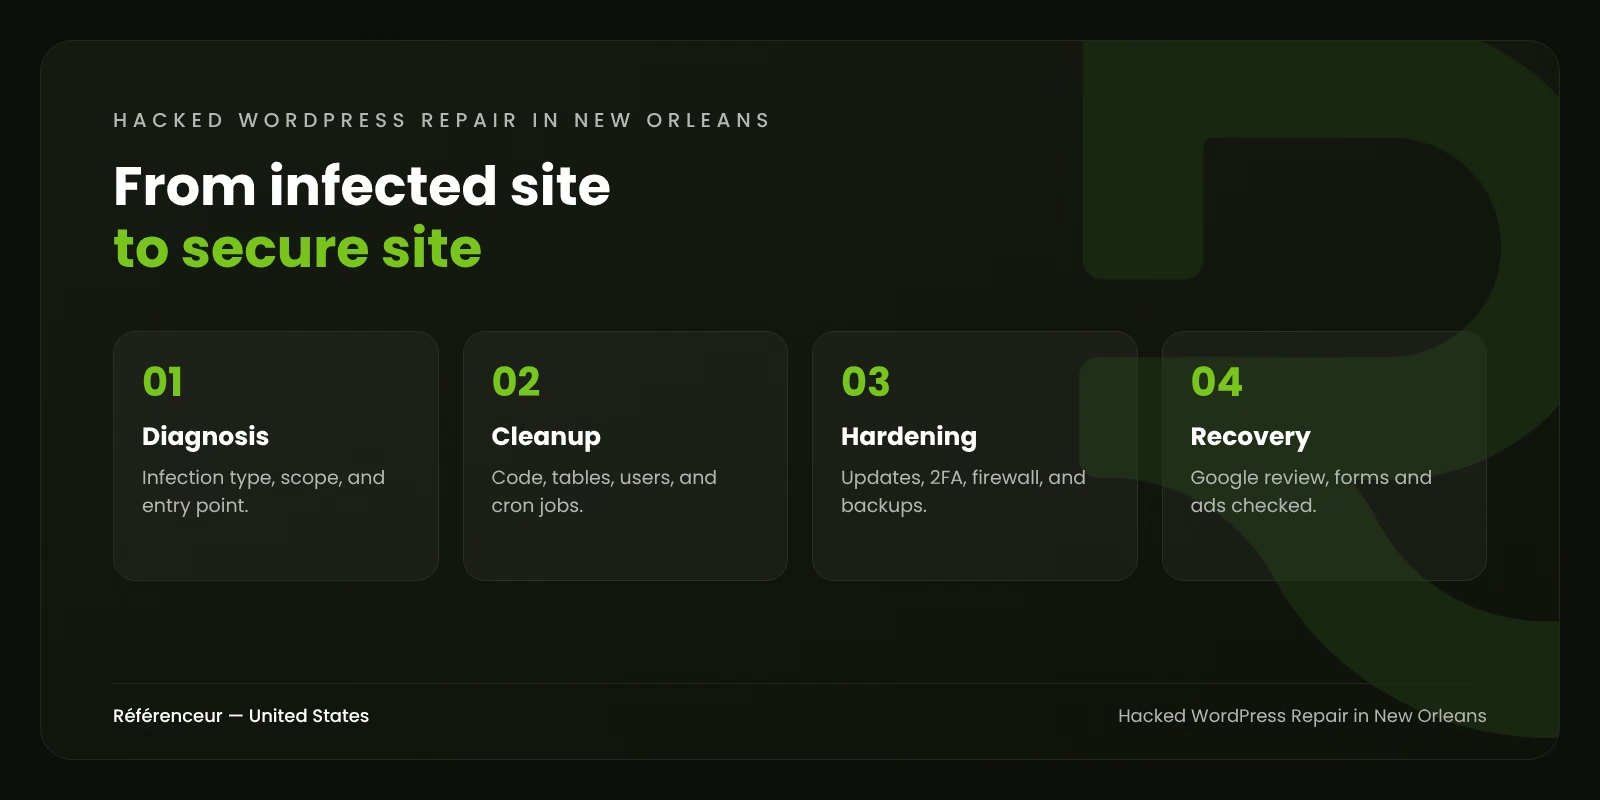
- Diagnosis: type of infection, scope, and likely entry point. We generally begin on the business day of your request.
- Cleanup: code, WordPress tables, user accounts, and cron jobs added by the attacker.
- Hardening: updates, passwords, two-factor authentication (2FA), firewall, and backups.
- Recovery: Google review request, form and ad checks, and ongoing monitoring.
A business website usually recovers within a few days. An online store or a heavily customized site can take longer, and we give you a realistic estimate at the diagnosis stage.
What Our Cleanup Covers
Hacked WordPress repair in New Orleans, as anywhere, isn’t just deleting malicious code. We need to understand how the attacker got in, then keep them out. Our work covers:
- A copy of the infected state, kept for analysis and incident documentation.
- Removal of backdoors, injected scripts, and files unknown to WordPress core.
- Database cleanup: spam links, redirects, and users created by the attacker.
- PHP, theme, and plugin updates, with abandoned components replaced.
- Stronger access: new passwords, 2FA, and permissions limited to what each user needs.
- A review request to Google and a check of your ads.
- Automated off-site backups and file change monitoring.
The cleanup also includes scanning older backups for malware. Our guide to removing malware from WordPress details the technical side. We sharply reduce the risk of reinfection without claiming absolute security: no honest provider can.
Why Choose Référenceur for Your Hacked Site
After a hack, you need someone who acts quickly and explains the situation clearly. We favor plain explanations and concrete evidence.
- Technicians who work remotely and don’t wait for an on-site visit.
- A clear report on the incident and the fixes, useful for leadership or your insurer.
- SEO and Google Ads expertise to limit lost visibility.
- A possible rebuild through our web design agency in New Orleans if the existing site is too fragile.
- European clients, including Lupulus, Menuiserie Rosen, Auto-école Georges, and Isolpur, in our case studies.
All our services are listed on our digital marketing agency in New Orleans page. We also help businesses in Texas: see our hacked WordPress repair in Houston.
Check Your Site Now
Has your WordPress site been acting strangely for a few days? Start a free check with our security scanner:
Get a free assessment of your hacked WordPress site in New Orleans. Our reply covers the extent of the infection, the probable entry point, and a repair plan quoted in U.S. dollars. Tell us what you are seeing, and we will reply as quickly as we can.
Hacked WordPress Repair FAQ for New Orleans
How Fast Can You Step In?
Urgent requests get priority, often the same day during our European business hours. Belgium is typically seven hours ahead of New Orleans, so a request sent late in your afternoon can often be handled before you wake up.
Will Google Push Us Down After the Incident?
A long infection can make pages disappear or trigger a warning. Acting in the first days significantly limits the impact. Rankings then take a few weeks to recover, with no guaranteed timeline.
What If Personal Data Was Exposed?
Louisiana law generally requires notifying affected residents within 60 days of discovering a breach of certain personal data, and notifying the Attorney General within 10 days of that notice. We document the incident; this isn’t legal advice, and your attorney determines your exact obligations.
What Does a Repair Cost?
It depends on the type of infection, the size of the site, and the hardening work. After the free assessment, we send a proposal in U.S. dollars. No paid work starts without your approval.
How Do We Prevent Another Attack?
Regular updates, off-server backups, individual accounts, and 2FA stop most common attacks. We can handle that maintenance monthly and send you a status report on updates, backups, and security alerts. Our WordPress security guide covers the basics.