 0498 70 98 60
Hacked WordPress Site Repair in Detroit: Back Online, Locked Down
A buyer at a Tier 1 supplier tells your sales manager that your website triggered a security warning on their corporate network. Or your careers page starts sending applicants to a scam. For a Detroit supplier, a hacked WordPress site can put a supplier relationship under review, because large manufacturers take cyber risk in their supply chain seriously.
Référenceur cleans and secures hacked WordPress sites remotely. We identify the entry point, remove malicious code from files and the database, close the vulnerability, and restore the site with stronger protection. A specialist explains each step in English or French, and your team receives a written report it can share with customers or insurers.
We have maintained and repaired WordPress sites for more than 15 years. Référenceur partners with Google and Microsoft Advertising and holds a 4.7/5 rating from 107 Google reviews. Get a Free Assessment: it costs nothing and tells you how serious the situation is.
Our free security scan below gives you a first reading in seconds, before you even contact us.
Detroit Businesses: Symptoms That Point to a Hack
Infections are designed to hide from administrators, and many show their effects only to visitors who arrive from Google or use a phone. Customers, Google, or your host usually notice first. These are the most common signs.
- Mobile visitors are redirected to gambling, pharmacy, or fake giveaway pages.
- Google lists pages in Japanese or counterfeit product offers under your domain.
- Your RFQ or job application forms stop delivering, or send spam.
- A browser shows a red “Deceptive site ahead” warning, or Search Console reports a security issue.
- Unknown administrator accounts appear, or plugins you didn’t install show up.
- Your web host suspends the account or blocks outgoing email.
- Google Ads disapproves your ads for malicious or unwanted software.
Before deleting anything or restoring an old copy, follow the first steps in our guide on what to do when your WordPress site is hacked. Preserving evidence helps us find the real cause faster.
Why a Hacked Site Hurts Detroit Suppliers
Automakers and Tier 1 suppliers increasingly assess the cybersecurity of their supply chain. A public sign of compromise, such as a malware warning on your domain, can raise questions you’d rather not answer in the middle of a sourcing decision.
Some customer questionnaires now ask directly whether you have had a security incident in the past year and how it was handled. A documented, professional response is far easier to explain than an infection that lingered for weeks. That’s why our process produces a clear written trail from the first diagnosis to the final check.
The commercial damage is immediate. RFQs stop arriving, job applications vanish, and Google Ads may suspend ads pointing to an infected site. Spam pages indexed under your domain can also undermine rankings that took years to earn.
Personal data adds legal questions. Michigan’s Identity Theft Protection Act (MCL 445.72) sets notification duties after certain security breaches. If your site collects data from Ontario residents, Canadian rules may also come into play. We provide the technical facts; your attorney determines your obligations, and this isn’t legal advice.
Our 4-Step Process
Acting in the right order prevents reinfection and preserves the evidence. Timing depends on the extent of the damage and on how quickly we receive access.
- Isolate and investigate: a snapshot of the infected site, then analysis of files, database, and access logs.
- Clean thoroughly: injected code, backdoors, rogue users, spam pages, and malicious scheduled tasks removed.
- Close and harden: the original weakness fixed, everything updated, all credentials changed.
- Confirm and monitor: final scans, a Google review request when needed, and ongoing alerts.
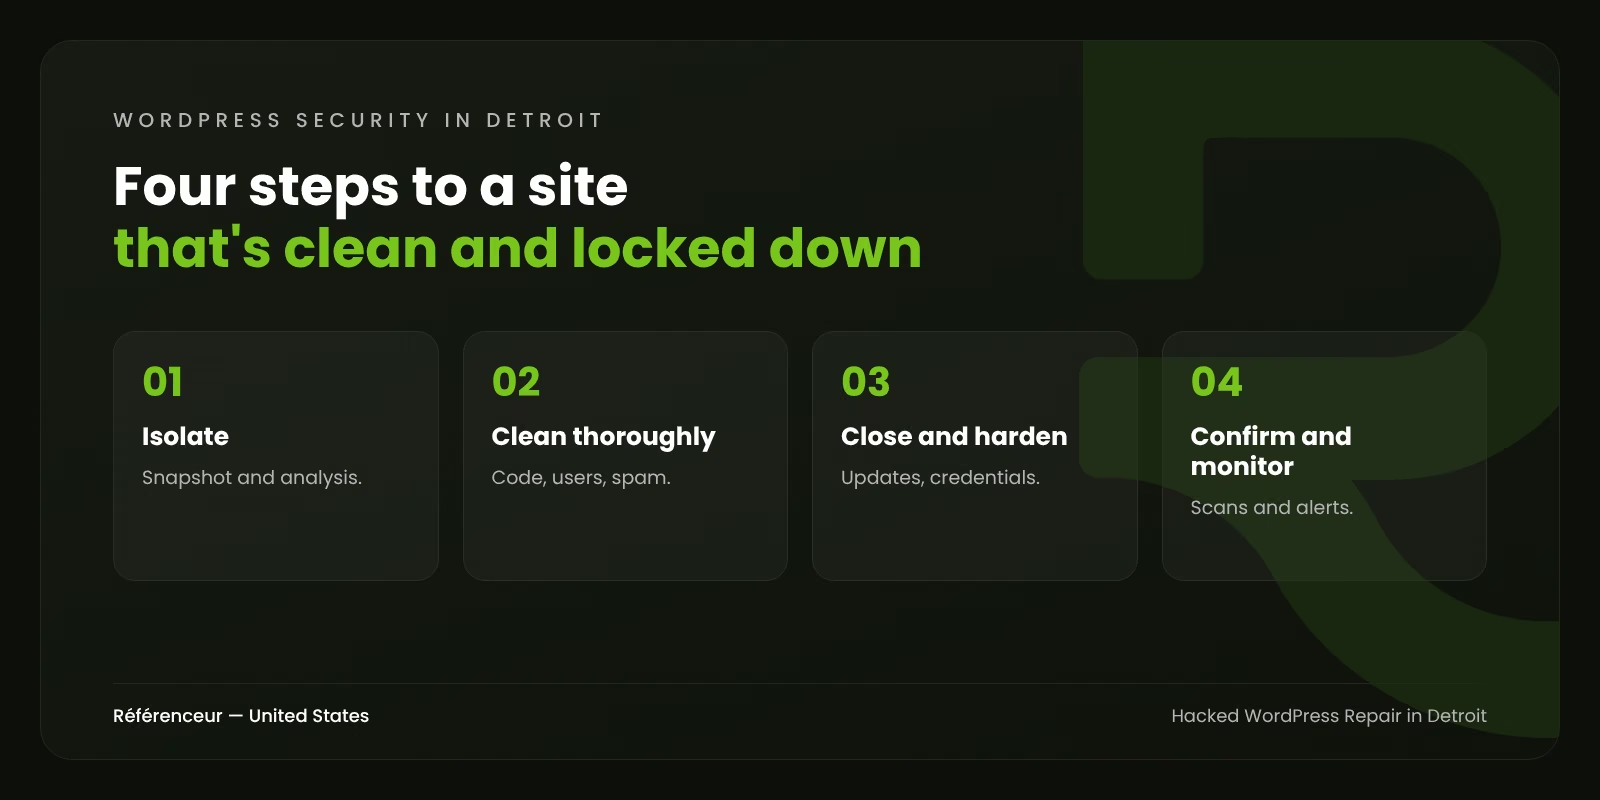
After each step you receive a brief written update by email, in plain English. The final report explains the cause, the fixes, and the measures we recommend.
What Our Detroit Hacked Site Cleanup Covers
| Area | What we handle |
|---|---|
| Investigation | Logs, file changes, and user activity reviewed to find how and when the attacker entered |
| Files | Malicious code and backdoors removed, core, plugins, and theme compared with clean versions |
| Database | Spam content, hidden links, and unauthorized accounts deleted |
| Updates | Everything brought current, abandoned plugins replaced, PHP moved to a supported version |
| Access control | New passwords and keys, two-factor authentication (2FA), least-privilege user roles |
| Protection | Web application firewall (WAF), login limits, file permission hardening |
| Backups | Automatic off-site backups with a tested restore procedure |
| Reputation | Spam URLs removed from Google, warnings lifted, email authentication checked |
Skipping the root cause means the attacker comes back. Our article on WordPress malware removal explains why quick fixes don’t hold. The complete service is on our national hacked WordPress site repair page.
Hacked WordPress in Detroit: From Corktown to Troy, Different Priorities
| Business profile | Priority | Our response |
|---|---|---|
| Automotive supplier with an RFQ portal | Reassure customers and restore inquiries | Incident report for customer security teams, forms and uploads checked |
| Engineering firm in Southfield | Protect confidential project files | Upload folders and integrations reviewed, access tightened |
| Restaurant or retailer in Corktown | Get the site and online orders back | Fast cleanup, ordering plugins checked, Google warnings lifted |
| Staffing agency in Dearborn | Secure applicant data | Application forms and resume storage reviewed, logs preserved for counsel |
| Distributor running Google Ads | Restart campaigns | Landing pages cleaned, ads resubmitted, tracking verified |
| Bilingual site serving Michigan and Ontario | Clean both languages and both markets | Every language version and country redirect checked |
Why Detroit Companies Choose Référenceur
Our security specialists work with our SEO and Google Ads teams, inside the same agency and with the same project lead. After cleanup, they handle spam URL removal, ranking recovery, and ad reapproval, so you don’t need three vendors to recover from one incident. Our hacked WordPress repair in Detroit covers the technical fix and the commercial recovery together.
Our specialists work from Belgium and Luxembourg, not Michigan. With hosting and wp-admin access, a cleanup moves just as fast from Europe, and the time difference lets work continue overnight in Detroit. Our references are European, including Auto-école Georges, Lupulus, Isolpur, and Menuiserie Rosen; see our case studies. Tell us what you’ve noticed, and read our WordPress security guide to prevent the next attack.
After the Cleanup: Strengthen Your Online Presence
An aging site stays vulnerable even once it’s clean. Our web design agency in Detroit can rebuild it on a maintained foundation. Every service for the region is on our Detroit digital marketing agency page. If a sister company in Illinois is affected, we also handle hacked WordPress repair in Chicago.
Unsure whether you’ve been hacked? Run our scan again.
Request a free assessment for hacked WordPress repair in Detroit. Send the address, and we identify the type of infection, its effects in Google, and the accounts and access points to secure first.
Detroit Hacked WordPress FAQ
Our Customer’s Security Team Is Asking Questions. Can You Help?
Yes. Our final report describes the incident, the cause, the data involved as far as the evidence shows, and the measures taken. It’s written so your team can share it with a customer’s security contact.
How Quickly Can You Begin?
As soon as we have hosting and WordPress administrator access. Recent infections are usually resolved faster than long-standing ones with multiple backdoors.
Is Restoring a Backup Enough?
Rarely. Recent backups may already contain the malware, and the vulnerability stays open. We scan any backup before restoring it, and we still close the original entry point afterward.
Do We Have to Notify Anyone?
It depends on the data and on where affected people live. Michigan, other states, and Canada each have their own rules. Our report gives your attorney the facts to decide.
How Much Does a Repair Cost?
It depends on the site’s size, the extent of the infection, and the number of weaknesses. We quote in dollars only after the free assessment, before any work starts.