 0498 70 98 60
Hacked WordPress Site Repair in Boston: Cleaned Up and Protected
Google is showing pharmacy pages under your domain. Visitors on mobile get sent to a scam site. Your host has just emailed a suspension notice. For a Boston company whose website supports sales, recruiting, or investor relations, a compromised site does damage every day it stays online.
Our hacked WordPress site repair service in Boston is handled entirely remotely. We clean the infection, find and close the vulnerability that was exploited, and bring the site back online in a healthy state. A dedicated technician keeps you informed throughout, in English or French.
Our technicians have repaired and maintained WordPress sites for more than 15 years. The agency carries a 4.7/5 rating based on 107 Google reviews and partners with Google and Microsoft Advertising. Get a free assessment of the affected site before any work is billed.
Want a quick first check? Our free tool below scans the visible security of your WordPress site in a few moments.
Spotting a Compromised Site Before It Costs Too Much
Many hacks stay invisible to the site owner, because attackers target visitors who arrive from Google or from a phone. These are the signs we find most often.
- Parasite content: pharmacy, casino, or counterfeit pages indexed under your domain.
- Hijacked visitors: redirects to dubious sites, sometimes only on mobile or only from Google.
- Suspicious email: your server relays spam, and your own messages get blocked by clients’ filters.
- Warnings: a red screen in the browser, a Search Console alert, or a suspension from your host.
- Technical signals: admin accounts nobody created, unknown files, unexplained slowdowns.
The business impact arrives fast. Google Ads can disapprove ads that lead to an infected site, which stops your campaigns. Indexed spam also drags on your rankings for weeks or months. If you’ve just discovered the problem, our guide on what to do when your WordPress site is hacked lists the first moves to make, and the ones to avoid.
There’s a regulatory side, too. In Massachusetts, 201 CMR 17.00 sets minimum standards for protecting residents’ personal information. It is based on Chapter 93H of the state’s General Laws, which also covers data breach notification. This isn’t legal advice; check with your attorney about what applies to you.
Hacked WordPress Repair in Boston: Different Organizations, Different Priorities
Urgency doesn’t look the same in every sector, even though each day counts. Here are situations we see among companies and organizations in the region.
| Organization profile | Main risk | Our priority |
|---|---|---|
| Biotech or medtech with an investor and press section | Credibility with partners and investors | Fast cleanup, checks on press releases and downloadable documents |
| CRO or lab services firm with quote forms | Lost requests and exposed contact data | Form and mailbox audit, rogue scripts removed, notifications restored |
| Software company running Google Ads | Disapproved ads and stalled pipeline | Cleanup, landing pages verified, ad reapproval followed through |
| Private school, training center, or language school | Parent and student accounts at risk | Access resets, role review, registration pages checked |
| Online store on WooCommerce | Card-skimming scripts and lost orders | Checkout inspected, injected JavaScript removed, priority restore |
| Firm with several brand websites | A whole fleet to secure | Inventory of installations, shared update schedule, grouped alerts |
In every case, we restore what brings in revenue first. The full security upgrade follows without delay.
What Our Hacked Site Cleanup Includes
A cleanup that leaves the hole open lasts a few days. Our service treats both the infection and its cause.
| Area | What we do |
|---|---|
| Diagnosis | Analysis of files, database, access logs, and user accounts |
| File cleanup | Malicious scripts and backdoors removed from core, theme, and plugins |
| Database cleanup | Infected posts, modified options, hidden links, and attacker-created users removed |
| Root cause | The exploited plugin, password, or server access identified and fixed |
| Updates | WordPress, theme, plugins, and PHP moved to maintained versions |
| Hardening | New passwords, two-factor authentication (2FA), file permissions, a web application firewall (WAF) |
| Backups | Automatic off-server backups with a tested restore |
| Search Console | Spam pages removed from the index, review request once the site is clean |
| Monitoring | Periodic comparison of files with their clean version and alerts on any change |
At the end, you receive a written report in English, or in French on request, covering the likely entry point, the actions taken, and our recommendations. It’s useful for your insurer or legal counsel. For background on why partial fixes fail, see our article on removing malware from WordPress. The complete service is described on our hacked WordPress site repair page.
Our 4-Step Process
Cleaning before understanding the attack is how infections come back. We always follow the same sequence, and its length depends on the infection.
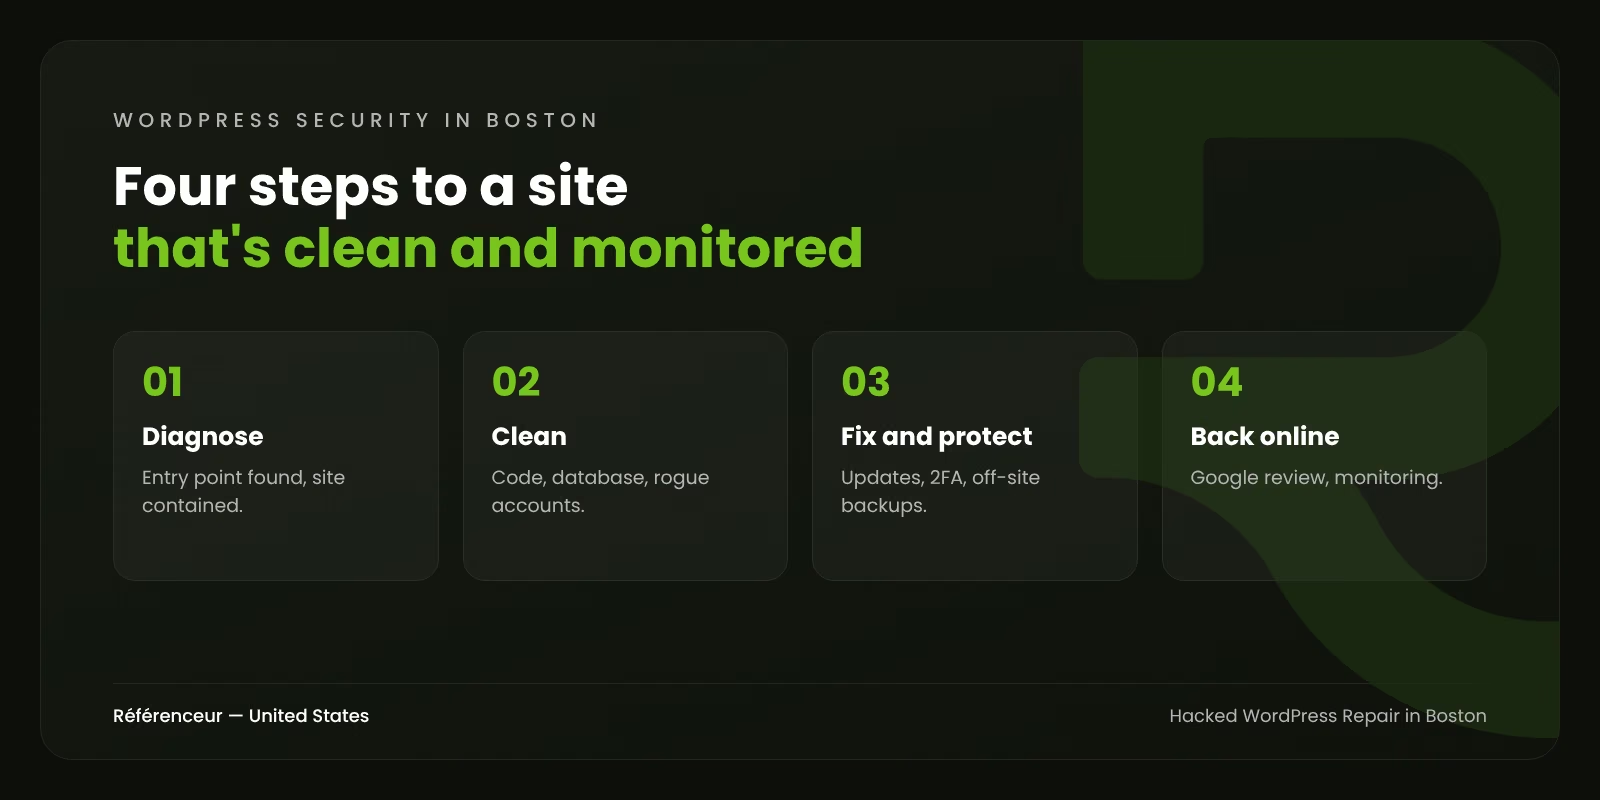
- Diagnose and contain: we identify the infection type, the likely entry point, and any exposed data, and put the site in maintenance mode if needed.
- Clean: files, database, and accounts are sanitized. Depending on the infection, allow from a few hours to a few days.
- Fix and protect: PHP, WordPress, and plugins updated, access secured, off-site backups set up.
- Back online: a Google review request if needed, indexing checks, and monitoring in the following weeks.
Google handles review requests at its own pace, which we don’t control. Sometimes it takes a few days, sometimes longer, and we keep watching for reinfection in the meantime.
Why Choose Référenceur for Your Hacked Site
Security, SEO, and Google Ads live in the same team here. After the cleanup, we check what Google actually sees of your site, get spam URLs removed, and follow the reapproval of suspended ads. You don’t have to coordinate several vendors during an already stressful week.
You deal with one technician from the first message to the final report, and you always know what’s been done, what’s pending, and what we need from you next. We work entirely remotely from Francorchamps and Wemperhardt, with no office in the U.S. For server work, being on site adds nothing.
The European clients behind our references include Lupulus, Isolpur, Menuiserie Rosen, and Auto-école Georges: browse our case studies. Then tell us the symptoms you’ve noticed for a fast first evaluation.
After the Cleanup: Rebuild and Prevent
An aging site with abandoned plugins stays fragile even after cleanup. Our web design agency in Boston can rebuild on a maintained foundation, and our WordPress security guide covers the habits that keep attackers out. All our local services are on our digital marketing agency in Boston page. If a sister company in Manhattan is hit, see our page on hacked WordPress repair in New York.
Not sure yet whether your site is affected? Run our free security scan.
Request a free assessment of your hacked WordPress site in Boston. We’ll identify the type of infection, its visible effect in Google, and the access points to secure first.
Frequently Asked Questions About Hacked WordPress Sites in Boston
How Quickly Can You Step In?
Urgent requests get priority, depending on our current workload, and we give you a precise timeline in the first exchange. Have your hosting, SFTP, and WordPress credentials ready: that saves the most time.
Will Our Search Rankings Suffer?
A long-running infection can push pages down or trigger a warning in Google. After cleanup and review, rankings generally come back gradually, though we can’t promise an identical return to where you were before.
Customer Data May Have Been Exposed. What Should We Do?
Notification laws vary by the state where affected people live. In Massachusetts, Chapter 93H applies. Talk to an attorney quickly; we’ll give them the technical facts: affected files, exposure window, and accessible data.
Can You Fix Our Site Without Being in Boston?
Yes. Everything happens on the server and in the WordPress dashboard. We only need the right access, which you can revoke when we’re done.
How Do We Avoid Getting Hacked Again?
Keep WordPress, your theme, and plugins updated, and remove what you don’t use. Use a maintained PHP version, unique passwords, and 2FA. Tested backups and monitoring complete the picture.